On this page
- Why critical payment data centres sit at the heart of the DPDP Act
- How the DPDP Rules regulate data centre and cloud security safeguards
- How data centre resilience maps to DPDP Act and Rules duties
- Where the 72-hour breach clock meets infrastructure incident response
- Our view: a six-point data centre and cloud readiness checklist before 13 May 2027
- Common questions
- In the news
- Sources
When Union Finance Minister Nirmala Sitharaman highlighted how the Reserve Bank of India's new greenfield data centre will strengthen India's critical payment infrastructure, the message reached far beyond central banking operations. Every regulated bank, non-banking lender, payment aggregator, unified payments interface switch and cloud service provider running high-volume financial transactions now operates under dual scrutiny: sector resilience mandates from financial regulators and the statutory security, processor-contract and log-retention obligations of the Digital Personal Data Protection Act, 2023 and the DPDP Rules, 2025 ahead of 13 May 2027.
Why critical payment data centres sit at the heart of the DPDP Act
Every digital payment transaction in India—whether a retail unified payments interface transfer, a recurring mandate, a card settlement or an instant loan disbursement—carries digital personal data alongside financial ledger entries. Payer and payee names, virtual payment addresses, linked mobile numbers, device identifiers and bank account numbers are all personal data relating to identifiable individuals.
Under the DPDP Act, the bank, payment institution or merchant that determines the purpose and means of processing that transaction data is the Data Fiduciary. The data centre operator, disaster-recovery host, cloud infrastructure provider or outsourced switch vendor that stores or routes those payment packets on the institution's instructions is a Data Processor. The statute makes a foundational rule clear: the Data Fiduciary remains legally responsible for complying with the Act and the Rules for all processing carried out on its behalf, regardless of any agreement to the contrary.
How the DPDP Rules regulate data centre and cloud security safeguards
Building a resilient data centre or migrating workloads to a multi-zone cloud region is no longer just an uptime target; from 13 May 2027 it is a statutory obligation backed by a penalty ceiling of up to ₹250 crore for failing to maintain reasonable security safeguards to prevent a personal data breach. The DPDP Rules spell out the minimum technical and organisational controls that every Data Fiduciary—and, by contract, every data centre and cloud Data Processor—must put in place:
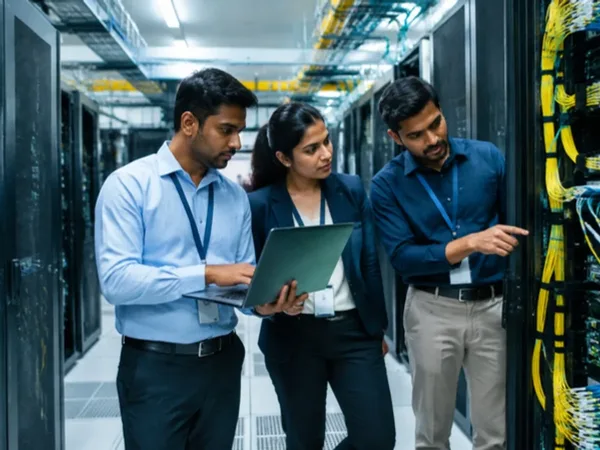
- Data security and encryption: Personal data stored on data centre disks, backup tapes, object storage buckets and replication links must be secured through appropriate encryption, obfuscation, masking or virtual tokens mapped to the primary identifier.
- Strict access control across computer resources: Administrative access to hypervisors, database clusters, payment switches and backup consoles must be governed by role-based access controls and multi-factor verification.
- Visibility and unauthorised-access detection: Every data centre and cloud environment must capture visibility into who accessed personal data through appropriate logs, monitoring and regular review so unauthorised access is detected early.
- Business continuity and disaster-recovery backups: Reasonable security safeguards explicitly include measures to ensure continued processing of personal data if confidentiality, integrity or availability is compromised—such as secondary data-centre failover and verified backups.
- Minimum one-year log retention: Specific processing logs and access records must be retained for at least one year to detect and investigate unauthorised access, alongside the mandatory one-year floor for traffic data and processing logs under the Seventh Schedule.
- Binding Data Processor contract clauses: Every hosting, colocation, cloud or payment-switch contract signed by a Data Fiduciary must include explicit provisions requiring the Data Processor to maintain reasonable security safeguards.
How data centre resilience maps to DPDP Act and Rules duties
The table below maps each layer of payment and data-centre infrastructure to the exact requirements that take effect on 13 May 2027:
| Data centre or payment layer | Operational risk in financial workloads | Required DPDP Act and Rules control |
|---|---|---|
| Primary and disaster-recovery server halls | Disk theft, unencrypted snapshots, or replication link interception between primary and secondary zones | Encrypt database volumes, backup archives and inter-zone links; tokenize account and card identifiers in application tables |
| Privileged infrastructure and database access | Shared root credentials, active contractor SSH keys, or unlogged production database queries | Enforce individual role-based accounts on every computer resource and record every privileged session in immutable audit logs |
| High-availability failover and backup recovery | Ransomware corruption or storage outage halting customer access, erasure workflows or payment verification | Maintain isolated backups and secondary-zone failover so personal data integrity and availability can be restored rapidly |
| Colocation, cloud and payment-switch vendors | Third-party data centre staff or managed-service engineers handling storage arrays without binding security clauses | Execute a written Data Processor agreement mandating equivalent technical safeguards, audit rights and immediate incident escalation |
| Security operations and log storage clusters | Rotating firewall, API gateway or database access logs after 30 or 90 days to save storage costs | Retain traffic data, access trails and processing logs for at least one year from each processing event before automated erasure |
| Incident response and regulatory reporting desk | Delayed coordination between data centre engineers and legal officers after a storage or API compromise | Wire infrastructure alerts into a 72-hour Data Protection Board reporting workflow alongside immediate notice to affected users |
Where the 72-hour breach clock meets infrastructure incident response
When a payment switch, cloud storage bucket or data centre server experiences unauthorised access, accidental exposure or destructive malware, the DPDP Rules require rapid escalation. Upon becoming aware of a personal data breach, the Data Fiduciary must notify each affected individual without delay in a concise, clear and plain manner—explaining what happened, the likely consequences, the mitigation steps taken, how the person can protect their interests, and the business contact for questions.
In parallel, the Data Fiduciary must notify the Data Protection Board of India without delay and submit a detailed six-point report within 72 hours of becoming aware of the incident covering updated facts, circumstances, reasons, mitigation steps, findings regarding the person responsible, and remedial measures. Failing to notify the Board or affected individuals carries a statutory penalty ceiling of up to ₹200 crore.
Our view: a six-point data centre and cloud readiness checklist before 13 May 2027
In our view, banking technology heads, infrastructure architects and compliance officers should complete six steps across their primary and disaster-recovery data centres before 13 May 2027:
- Map every data centre, cloud region, colocation facility and disaster-recovery site that stores or routes customer personal data, and record whether each environment is operated in-house or by a third-party Data Processor.
- Verify that encryption at rest, encryption in transit, field-level masking and virtual tokenisation are active across both primary production databases and secondary disaster-recovery replicas.
- Eliminate shared administrator logins across hypervisors, storage consoles and database clusters, and review privileged access logs on a scheduled monthly cadence.
- Upgrade log-storage pipelines so application, database, API gateway and network traffic logs are retained for at least one year from the date of processing.
- Audit every colocation, cloud hosting and managed-infrastructure contract to ensure it contains a binding Data Processor clause requiring reasonable security safeguards and immediate breach escalation.
- Run a joint tabletop exercise between your data centre engineering team and legal counsel to verify that an infrastructure alert can be triaged, contained and documented within the 72-hour Data Protection Board reporting window.
Common questions
Who is legally responsible under the DPDP Act when a bank or payment app uses a third-party data centre or cloud provider?
The bank or payment platform that determines the purpose and means of processing is the Data Fiduciary, while the data centre or cloud host is a Data Processor. The Data Fiduciary remains legally responsible for complying with the Act and the Rules across all processors, and may engage a processor only under a valid contract.
Does the DPDP Rules security standard require disaster-recovery backups and business continuity?
Yes. Reasonable security safeguards explicitly include measures to ensure the continued processing of personal data in the event of a loss of confidentiality, integrity or availability, such as disaster-recovery replicas and verified backups.
How long must payment platforms and data centres keep traffic data and security logs?
Data Fiduciaries must retain personal data, associated traffic data and processing logs for a minimum period of one year from the date of processing for the detection and investigation of unauthorised access and for the statutory purposes in the Seventh Schedule.
How fast must a data centre or payment breach be reported to the Data Protection Board of India?
Upon becoming aware of a personal data breach, the Data Fiduciary must notify each affected individual and the Data Protection Board without delay, and submit a detailed six-point report to the Board within 72 hours.
Next steps
- Check whether the DPDP Act applies to your business, free, in a few clicks
- How-to 04: Set the rules, in the toolkit
- How-to 09b: Sign the vendor contract, in the toolkit
- How-to 11: When something goes wrong, in the toolkit
- The free duties list, every duty in plain words
In the news
RBI’s new data centre to strengthen India’s critical payment infrastructure: FM Sitharaman
Union Finance Minister Nirmala Sitharaman highlighted how the Reserve Bank of India's new data centre strengthens the resilience and security of India's critical payment systems.
DPDP Act & Rules takeaway: Our article maps data-centre and cloud resilience to DPDP Section 8(5) and Rule 6 security safeguards, continuity backups, binding Data Processor contracts, and 1-year log retention.
View statutory briefing illustration
 Source & Courtesy Reference: The Tribune (original report)
Videos
Sources
Every section, rule and date above was checked against the official text on 25 Oct 2026.
Digital Personal Data Protection Act, 2023 (No. 22 of 2023)
- Section 8(1)Data Fiduciary remains responsible for processing by Data Processors
- Section 8(2)Engaging a Data Processor only under a valid contract
- Section 8(5)Duty to protect personal data by taking reasonable security safeguards
- Section 8(6)Duty to notify the Board and each affected individual of a personal data breach
- The Schedule, items 1 and 2Penalty ceilings: up to ₹250 crore for security safeguards breach; up to ₹200 crore for failure to report a breach
DPDP Rules, 2025 (G.S.R. 846(E), 13 November 2025)
- Rule 6(1)Encryption, masking, access control, visibility logs, continuity backups, one-year logs and processor contracts
- Rule 7(1)Immediate plain-language breach intimation to each affected individual
- Rule 7(2)Immediate Board intimation and detailed six-point report within 72 hours
- Rule 8(3)Minimum one-year retention of personal data, traffic data and logs
- Seventh ScheduleState and statutory purposes for minimum one-year retention of data and logs
Notifications
- G.S.R. 843(E), clause (c)Substantive security, retention and breach duties in force from 13 May 2027
A drafting aid. Get legal advice for your situation. This article explains the published text of the Act and the Rules.