With your permission, we use Google Analytics to see which pages help visitors. It sets cookies and sends what you do on this site, and your IP address, to Google, possibly outside India. If you choose Reject, nothing is sent to Google. You can change your choice at any time from “Cookie and consent settings” at the bottom of every page.
What we collect: pages and topic; referring link; Buy, button, news, FAQ and share clicks, and where; preview, video plays; articles read, how far; scrolling; links you click to other sites (full address); processing map start, finish, business type; device, operating system, browser, screen size, language, approximate location; cookie ID. Google receives your IP address.
Why: to count visits and improve the site. Google processes it for us, possibly outside India, keeping it 14 months. No advertising use.
Withdraw: “Cookie and consent settings” in any footer, as easily as saying yes.
13 walkthrough videos (26 min) + Free updates till May 2027Watch in your dpdpa.support LMS portal · licensed for your business or 1 named CA/CS client
256-Bit Encrypted Checkout on dpdpa.support
Official Gazette G.S.R. 846(E) Citations
Instant Word & Excel ZIP + GST Invoice
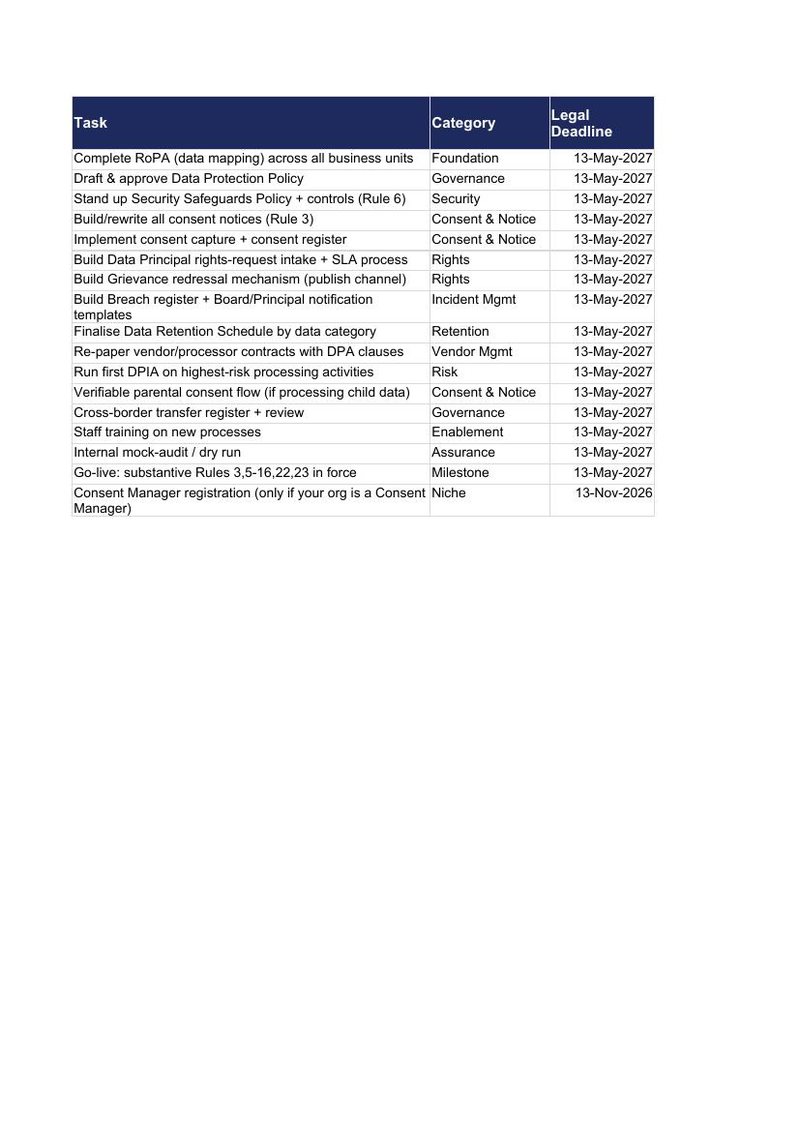
Key dates
13 Nov 2025DPDP Rules notified
13 Nov 2026Consent Manager registration rule in force
13 May 2027Data Fiduciary duties and penalties apply
The law
Until DPDP duties and penalties apply (13 May 2027)Data Fiduciary duties and penalties apply from 13 May 2027.DAYS TO GO0before 13 May 202700hrs00min00sec
Built for Indian businesses
Built for founders, IT leads and compliance teams
Founders and owners who decide what data the business collects and why.
IT and operations leads who run the systems and the vendors.
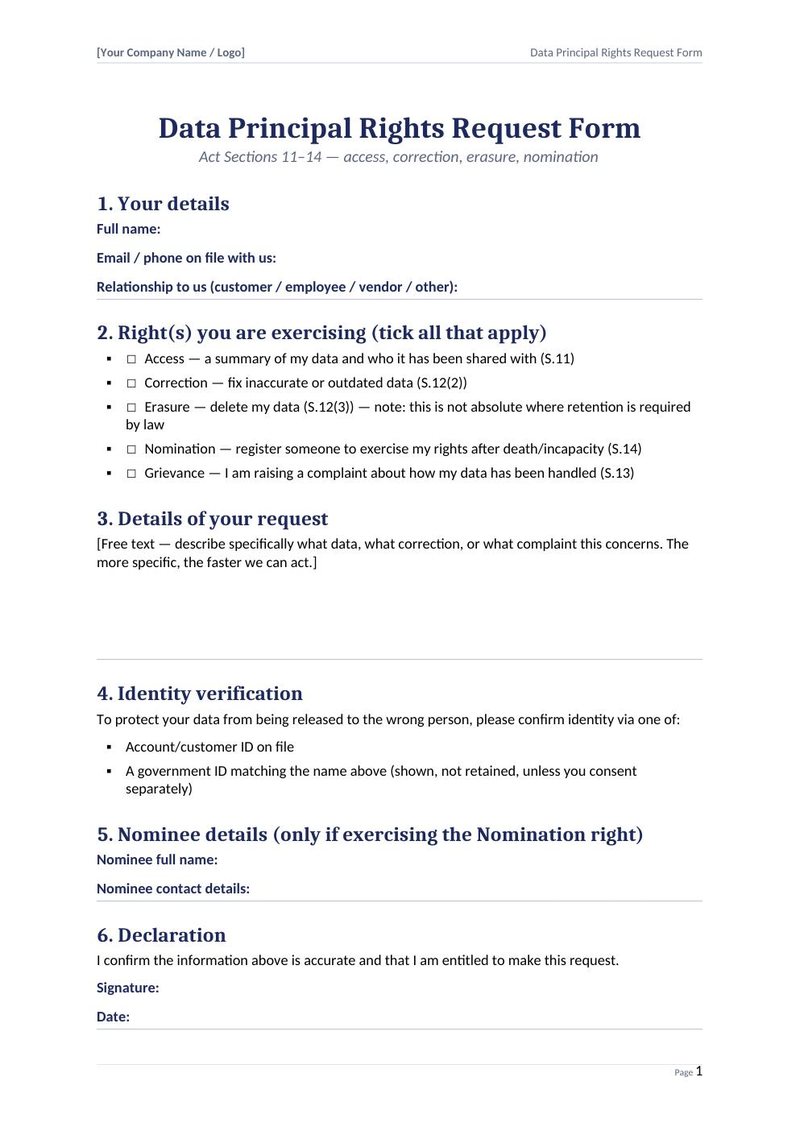
Compliance and support leads who answer people’s requests about their data.
Stock photographs for illustration. They are not our team or our customers.
Step 1 of 3 · 8 sector toolkits
1. Pick your sector
Tap your industry below. Your RoPA, Policy, Notice, Retention, DPIA, Vendor & Transfer files arrive pre-populated with built-in Excel formulas and 13 videos.
1
Tap your sectorPrefilled RoPA & 12 templates
2
Pay ₹2,999One-time incl. GST on Razorpay
3
Swift startZIP, Excel rubrics & 13 videos
Website & SaaS toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for B2B websites, SaaS apps, cloud software, and service businesses: enquiry forms, user accounts, billing, support tickets, and employee HR.
Personal dataName, email, role, auth logs, session & audit logs
Retention & erasure (Step 06)Erase on account closure unless required by law + 1-year log floor
ACT-03Legitimate Use - S.7(a) (voluntary provision)
Subscription billing, GST invoicing & payment records
Personal dataBilling contact, GSTIN, invoice history, gateway reference
Retention & erasure (Step 06)72 months (6 years) from annual return due date for GST invoices (CGST Act s.36); 8 years for corporate books of account (Companies Act s.128)
ACT-04Consent (S.6)
Product newsletter, webinar & marketing updates
Personal dataName, email, subscription preferences, consent timestamp
Personal dataEmployee ID, PAN, bank account, attendance, emergency contact
Retention & erasure (Step 06)Duration of employment + statutory labour/tax period
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Retail & E-Commerce toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for D2C brands, online stores, and omnichannel retailers: order fulfilment, UPI/card gateway logs, CGST s.36 72-month (6-year) invoice retention, returns & support, loyalty marketing, and store staff.
Personal dataStaff name, PAN, bank details, biometric/shift attendance
Retention & erasure (Step 06)Tenure + statutory EPF/ESI and tax retention period
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Finance & Fintech toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for fintechs, NBFCs, wealth platforms, and insurers: KYC verification, credit/policy underwriting, transaction monitoring, account servicing, and HR.
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Health & Clinics toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for hospitals, clinics, diagnostics, and digital health apps: patient registration, clinical & lab records, paediatric parental consent (Rule 10 & Fourth Schedule), emergency care, insurance billing, and clinical staff.
ACT-04Legitimate Use - S.7(a) (voluntary provision)
TPA / health insurance cashless claims & hospital billing
Personal dataPolicy number, claim form, discharge summary, GST/invoice log
Retention & erasure (Step 06)72 months (6 years) for GST records (CGST Act s.36); 8 years for corporate books of account & insurance audit
ACT-05Legitimate Use - S.7(i) (employment)
Doctors, nurses & hospital staff HR and credentialing
Personal dataRegistration number, PAN, bank details, shift roster, health check
Retention & erasure (Step 06)Tenure + statutory medical establishment and labour period
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Education & EdTech toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for schools, universities, coaching institutes, and EdTech platforms: includes the dedicated Children's Verifiable Parental Consent Procedure (verifiable-consent-procedure.docx) & Parent-Guardian Verification Ledger (consent-record.xlsx) under S.9(1), Rule 10 & Fourth Schedule, plus admissions, LMS, and faculty HR.
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Data Centres & Cloud toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Who this pack is for: Cloud, VPS, colocation, and managed-IT providers act mainly as Data Processors for client workloads (bound by S.8(2) DPAs, Rule 6(1) security safeguards, and 1-year logs), while acting as Data Fiduciaries for their own B2B customer accounts, billing, NOC/facility biometric & CCTV access, and engineers. Covers both roles.
Personal dataBilling contact, GSTIN, PO/invoice records, payment references
Retention & erasure (Step 06)72 months (6 years) from annual return due date for GST invoices (CGST Act s.36); 8 years for corporate books of account (Companies Act s.128)
ACT-05Legitimate Use - S.7(i) (employment)
NOC engineers, facility staff & contractor HR records
Personal dataEmployee ID, background verification, PAN, bank details, shift logs
Retention & erasure (Step 06)Tenure + statutory labour and tax retention
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Media & Publishing toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for digital publishers, OTT platforms, newsrooms, and agencies: subscriber accounts, newsletter/push consent, ad-tech consent, editorial/contributor contracts, and staff.
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Social & Gaming toolkit ₹2,999 incl. GST per sector · one time · free updates till May 2027
Prefilled for community apps, social platforms, and online gaming: includes the dedicated Children's Verifiable Parental Consent Procedure (verifiable-consent-procedure.docx) & Parent-Guardian Verification Ledger (consent-record.xlsx) under S.9 & Rules 10–12, plus Third Schedule 3-year inactivity erasure + 48-hour warning, moderation, and HR.
Owned by CynorSense Solutions Pvt. Ltd. · single-sector licence for your business or 1 named CA/CS client (₹2,999 incl. GST per sector · includes free updates till 13 May 2027).
Why pay ₹2,999 when free templates exist?
Built for Indian law. Prefilled for your sector.
Free privacy templates hand you blank tables and European GDPR rules. Every sector pack arrives pre-populated with Indian statutory numbers, Excel formulas, and walkthrough videos.
CGST Act s.36 · Rule 8(3)
1. Sector-Prefilled Rows & Indian Tax Rules
Pre-populated for your sector — including 72 months (6 years) under CGST Act s.36 for tax invoices and the 1-year log floor under Rule 8(3).
Watch 13 short screen recordings inside your dpdpa.support LMS portal showing every workbook tab and bracket in order.
DPDP Act s.6, s.7 & s.9 / Rule 10
4. Indian Law + Children’s Parental Consent
Enforces Indian S.6 & S.7 dropdowns and includes the Children’s Verifiable Parental Consent Procedure (verifiable-consent-procedure.docx) & Record (consent-record.xlsx).
Updates till May 2027 · CA/CS Ready
5. Free Updates till May 2027 + CA/CS Licence
Includes free updates until 13 May 2027 for your business or 1 named CA/CS client (or unlock all 8 sectors in the ₹29,999 Master Pack).
Step 2 of 3 · Inside your ZIP
2. Preview the 12 templates
Editable Word policies and notices plus Excel trackers with built-in formulas, Indian-law dropdowns and Dashboards.
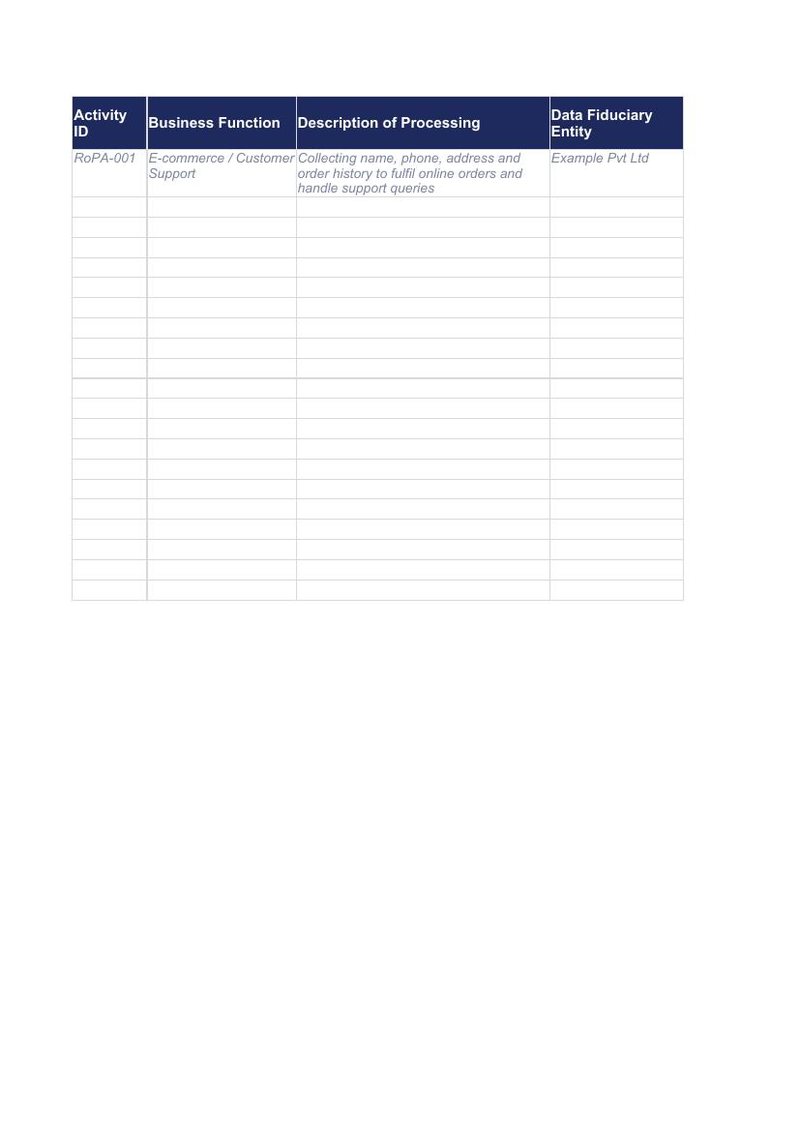
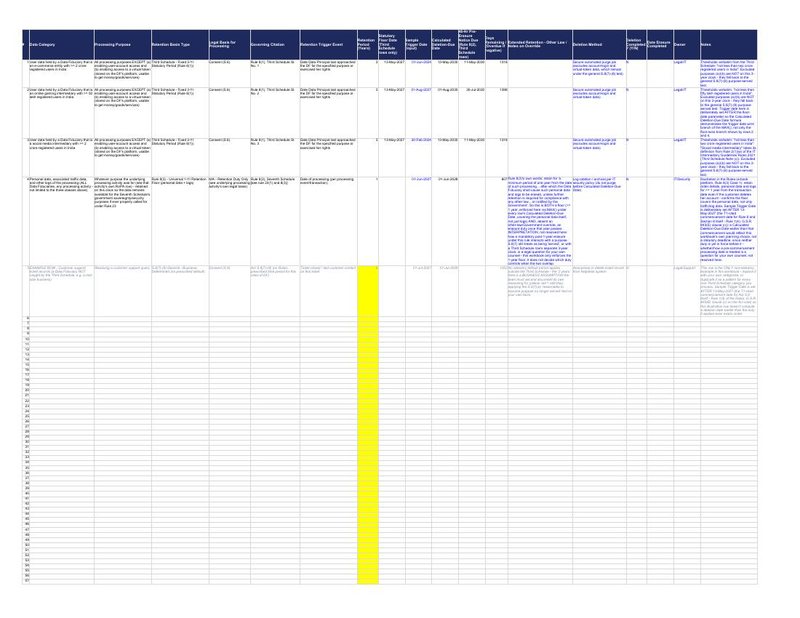
Internal 20-column master register of every personal data activity.
Must include:
Activity ID, purpose, data categories, Indian legal basis (Consent (S.6) or Legitimate Use - S.7(a) to S.7(i)), processors, storage, and retention link.
Boundary:
Never copy a GDPR RoPA ("Legitimate Interest" and "Contractual Necessity" do not exist in the DPDP Act) or publish your internal RoPA as a public notice.
Activity-linked schedule setting erasure triggers and mandatory audit-log retention windows.
Must include:
Primary erasure trigger (s.8(7)), statutory overrides (72 months / 6 years for GST tax invoices under CGST Act s.36; 8 years for corporate books of account under Companies Act s.128), mandatory 1-year minimum log floor (Rule 6(1)(e) & Rule 8(3)), and Third Schedule rules.
Boundary:
Do not delete processing and traffic logs immediately on account deletion; Rule 6(1)(e) and Rule 8(3) require at least 1 year of log retention.
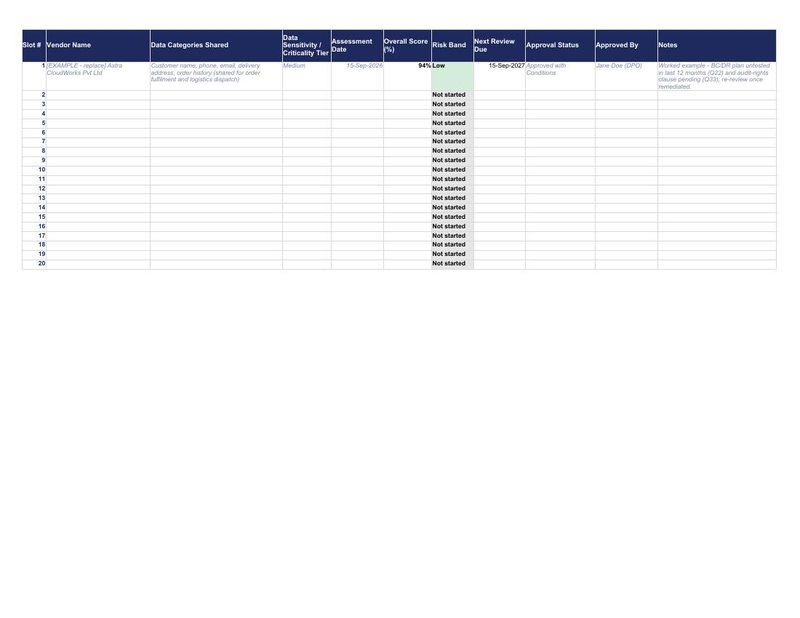
Processor security screening workbook (Step 09) and bilateral Data Processing Agreement (Step 09b, Section 8(2)).
Must include:
Processing scope, all seven Rule 6(1) security controls passed to the processor (Rule 6(1)(f)), rapid breach reporting for your 72-hour Board deadline, and erasure cascade.
Boundary:
A plain NDA does not satisfy Section 8(2) or Rule 6(1)(f). Under Section 8(1), the Data Fiduciary remains liable for processor failures.
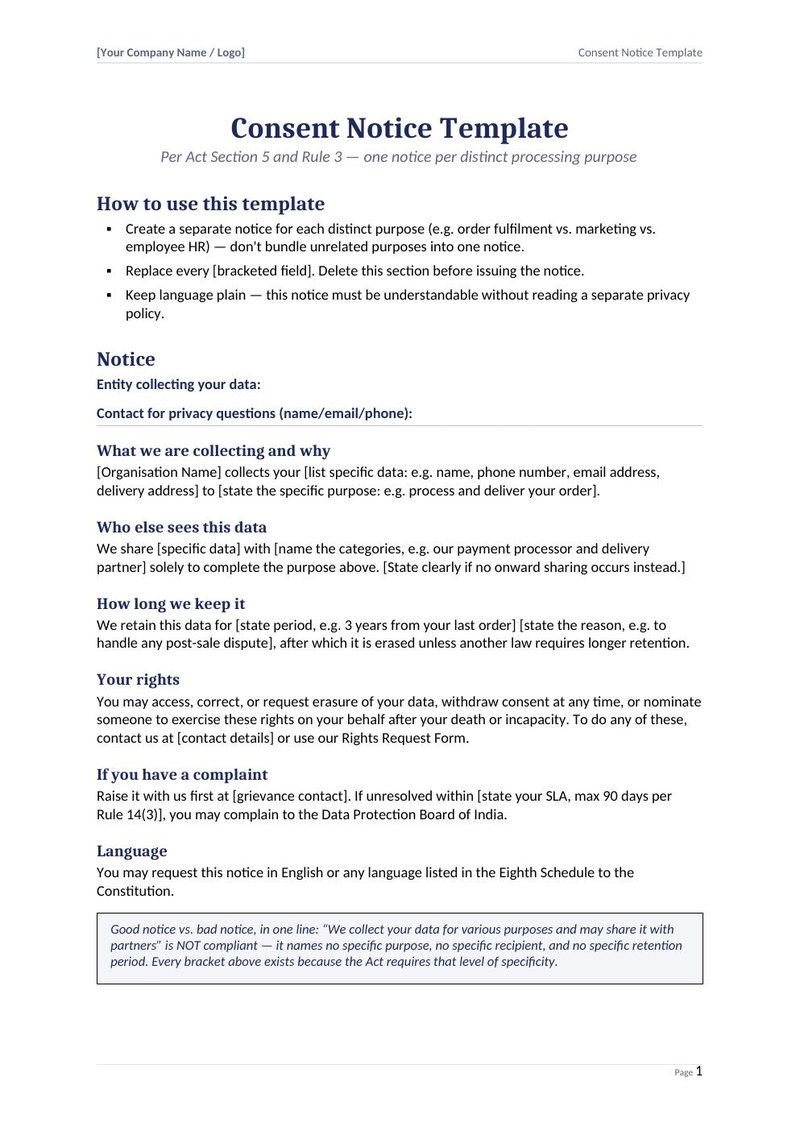
Operational registers for the 90-day grievance ceiling (Rule 14(3)) and two-stage breach notices (Rule 7).
Must include:
90-day countdown formulas, zero-threshold breach log, immediate Board intimation + 72-hour detailed report tracker, and Data Principal breach notice.
Boundary:
The Indian DPDP Act has no minimum size threshold: every personal data breach must be notified to the Board and affected individuals.
Inside a template
See how a prefilled template works
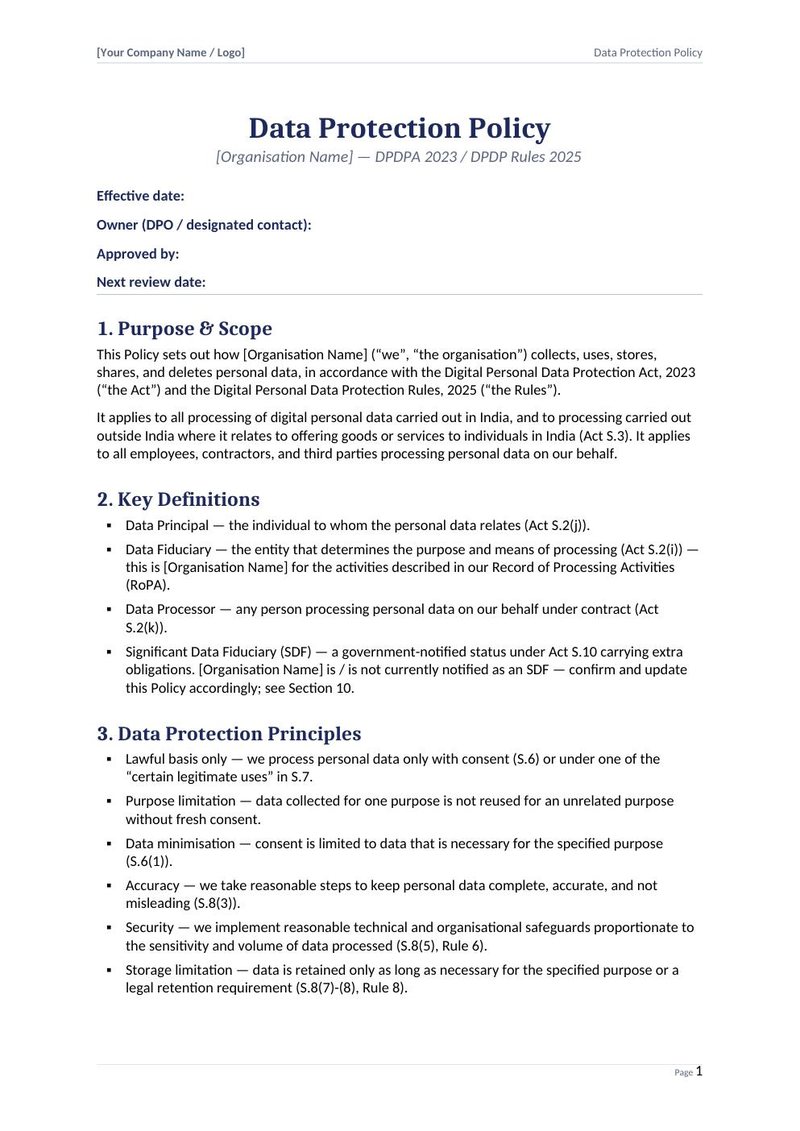
Each video moves through the real document, one section at a time, and shows where every input comes from. Here is page one of the Data Protection Policy (Step 04).
From how-to 04: effective date, owner, approver and next review, filled from the Compliance Timeline.
Every bracket is yours
1Every bracket is yours
Type your company name into the header and the title. The worked example uses a fictional online store.
2Four fields, filled from your plan
Effective date, owner, approver and next review. The dates and owners come from your Compliance Timeline in step 02.
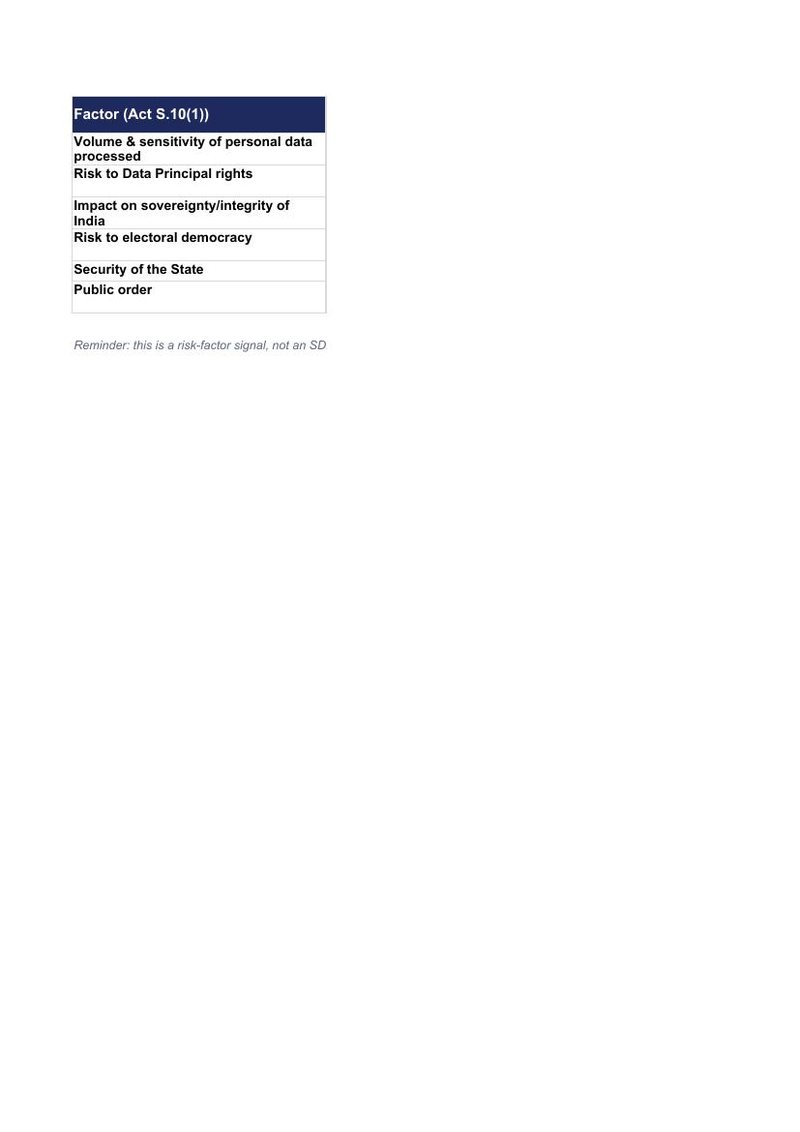
A DPO is required only for a notified Significant Data Fiduciary
3Scope and roles
The policy opens with its scope, then defines the roles and asks whether you are a Significant Data Fiduciary, a status only the Central Government can give by notification.
4Seven principles
From lawful basis to accountability. Five cite the Act; two are your own commitments. Keep all seven.
Lawful basis: consent, or a legitimate use the Act lists
Step 3 of 3 · Guided rollout
3. Follow the 12-step rollout order
13 walkthrough videos guide you step by step so the same activity IDs, vendors, and dates flow cleanly across every document.
Special multi-framework pack bridging Indian DPDPA compliance with ISO 27001/27701, ISO 27018, NIST Privacy, EU/UK GDPR, and US CCPA/CPRA using 8 policies and gap workbooks.
Word
ft-gp-01-iso27701-privacy-information-management-policy.docxMaster PIMS governance policy aligned with ISO 27701 & DPDP Act
Word
ft-gp-02-privacy-by-design-and-default-engineering-policy.docxSDLC privacy gates, data minimisation & release checklist
Excel
ft-gp-03-iso27701-pims-gap-assessment-and-action-tracker.xlsxISO 27701 PIMS control readiness workbook with Dashboard
Excel
ft-gp-04-iso27018-cloud-pii-protection-gap-assessment.xlsxISO 27018 public-cloud PII processor control assessment workbook
The Act sets maximum penalty ceilings by breach category. The Board may impose a penalty after an inquiry finds a significant breach and gives the person an opportunity of being heard.
Check which of the 19 legal duties your business already covers.Step 01 maps all 19 legal duties and 1 good-practice item against their citations and penalty ceilings.
Choose your sector, pay once, and get your prefilled sector RoPA, all 12 core Word & Excel templates with built-in scoring rubrics, 3 bonus tools, and all 13 training videos delivered by email right after payment.
The price includes GST (₹2,999 incl. GST per selected sector toolkit). To get a GST invoice, email us your billing name, address and GSTIN. No refunds: the toolkit is digital and delivered right after payment.
Your selected sector toolkit ZIP and program invitation arrive by email after payment. Check spam too.
Questions
Questions and answers
Does the DPDP Act apply to my business?
Ask two questions. Do you collect personal information digitally, such as names, phone numbers or emails, even in a spreadsheet on a laptop? Is any of it stored on a computer, phone, app or the cloud? If yes, and you process it in India or to offer goods or services to people in India, the law is built to cover you, unless an exemption applies, such as data an individual processes for a personal or domestic purpose, data the person has made public, or one of the other exemptions the Act lists. Step 01 starts with exactly these two questions.
A DPO is mandatory only for a business the Central Government notifies as a Significant Data Fiduciary. Every Data Fiduciary must publish the contact of someone able to answer questions about its processing. Steps 04 and 12 cover both.
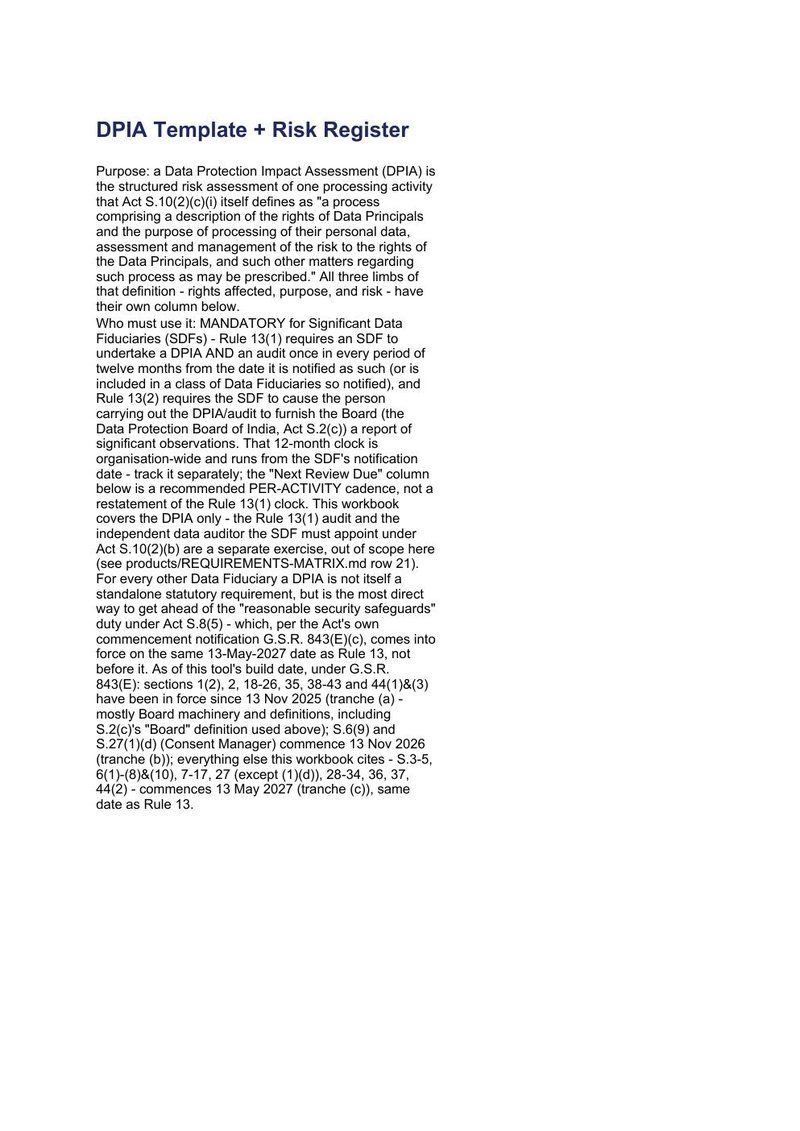
The Act requires a periodic Data Protection Impact Assessment only from Significant Data Fiduciaries. The toolkit recommends one for any high-risk activity and step 08 shows how to run it.
The Rules cap the grievance response period you publish at ninety days. The rights tracker applies the same 90-day target to every request type as its own choice, and turns a request red when fewer than 15 days remain.