With your permission, we use Google Analytics to see which pages help visitors. It sets cookies and sends what you do on this site, and your IP address, to Google, possibly outside India. If you choose Reject, nothing is sent to Google. You can change your choice at any time from “Cookie and consent settings” at the bottom of every page.
What we collect: pages and topic; referring link; Buy, button, news, FAQ and share clicks, and where; preview, video plays; articles read, how far; scrolling; links you click to other sites (full address); processing map start, finish, business type; device, operating system, browser, screen size, language, approximate location; cookie ID. Google receives your IP address.
Why: to count visits and improve the site. Google processes it for us, possibly outside India, keeping it 14 months. No advertising use.
Withdraw: “Cookie and consent settings” in any footer, as easily as saying yes.
For Acme Technologies Pvt. Ltd., administered by the CISO / Data Protection Officer: A written risk assessment of risks to the security, confidentiality and integrity of customer
2.1 Control Implementation & Quantitative Scoring Thresholds for Acme Technologies Pvt. Ltd. across production systems and sub-processors...
3.2 Audit Evidence Collection, Immutable 365-Day Telemetry & Board Sign-Off Matrix under CISO / Data Protection Officer...
🔒 Purchaser-Only GRC Vault · 2-Hour Signed Email Link Delivery
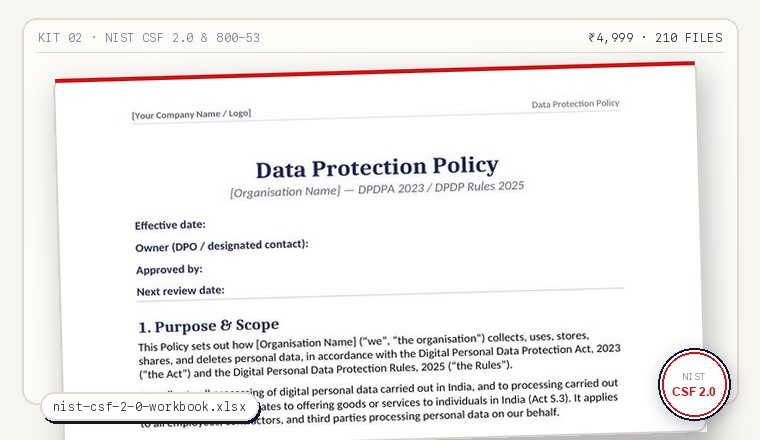
Unlock the Full Editable cynorsense-glba-safeguards-risk-assessment-template.xlsx inside the NIST CSF 2.0 & Core Security Policy Toolkit
Enterprise security governance policy & operational control template. For copyright and security protection, templates are never exposed for direct public download. Purchasing this toolkit emails a unique signed download link valid for 2 hours max (up to 10 download requests per user; contact [email protected] if additional dispatches are needed).
How This Template Accelerates Your Audit & Career
A written risk assessment of risks to the security, confidentiality and integrity of customer information, as the FTC Safeguards Rule (16 CFR Part 314) requires of financial institutions.
List each system/process and its risks, rate likelihood and impact, and record the safeguard. The Safeguards Rule requires the risk assessment to be written; this gives you that.
Tap your industry below. Your India DPDPA 2023 pack (₹2,999) is pre-mapped to your sector, and we will pair the exact domain standards that apply to your industry:
What level of compliance readiness do you want to deploy for Website, SaaS & IT?
Review your tailored stack before payment. Your India DPDPA 2023 pack is customized for your sector, and our Global Standard Toolkits provide universal domain-ready policies and Excel workbooks you can deploy across your organization immediately:
Selected Stack Total (incl. 18% GST)₹2,999
🔒 2-Hour Rotating Signed Email Delivery (Zero Direct Public Downloads):Templates are never exposed for direct public download. Immediately after payment (and each time you request a download in your Purchaser Vault), we email a unique signed link valid for 2 hours max (up to 10 download requests per user; contact [email protected] if additional dispatches are needed).