

Framework toolkit
Enterprise CISO Core Security Policies & Registers Toolkit
44 editable templates: 28 Word, 16 Excel. Each one is listed below with its sections, and 42 of the 44 with page 1.
₹4,999 incl. GST
Review cart (0)- 44 files you can edit in Word and Excel
- UPI, card or netbanking through Razorpay
Three of the 44. Open one to see its full outline.
What you get
All 44 files in this toolkit
Registers, logs and trackers11
-
 Data Breach Register
A register of ALL personal-data breaches — required by GDPR Art.
-
 Document and Record Control Procedure
✎ Apply it to this whole template set as your controlled documentation.
-
 It Asset Inventory
A hardware and software/SaaS inventory — the foundation of CIS Controls 1 & 2.
-
 Legal and Regulatory Requirements Register
A register of the laws, regulations and contract terms you must comply with (ISO 27001/22301 require this).
-
 Phishing Simulation Tracker
A tracker for phishing-simulation campaigns and their results over time.
-
 Privacy Notice Register
A register of all your privacy notices, their versions and review dates.
-
 Risk Register
A living cyber risk register with automatic likelihood × impact scoring.
-
 Security Awareness Training Tracker
A matrix tracking which employees completed which awareness modules.
-
 Security Incident Log
A register to record and track security incidents from detection to closure.
-
 Vendor Management Tracker
A central inventory of your suppliers, their data access and review status.
-
 Vulnerability Remediation Tracker
A tracker that logs vulnerabilities and enforces remediation SLAs.
Assessments and checklists3
-
 Employee Offboarding Security Checklist
A security checklist to run when an employee or contractor leaves.
-
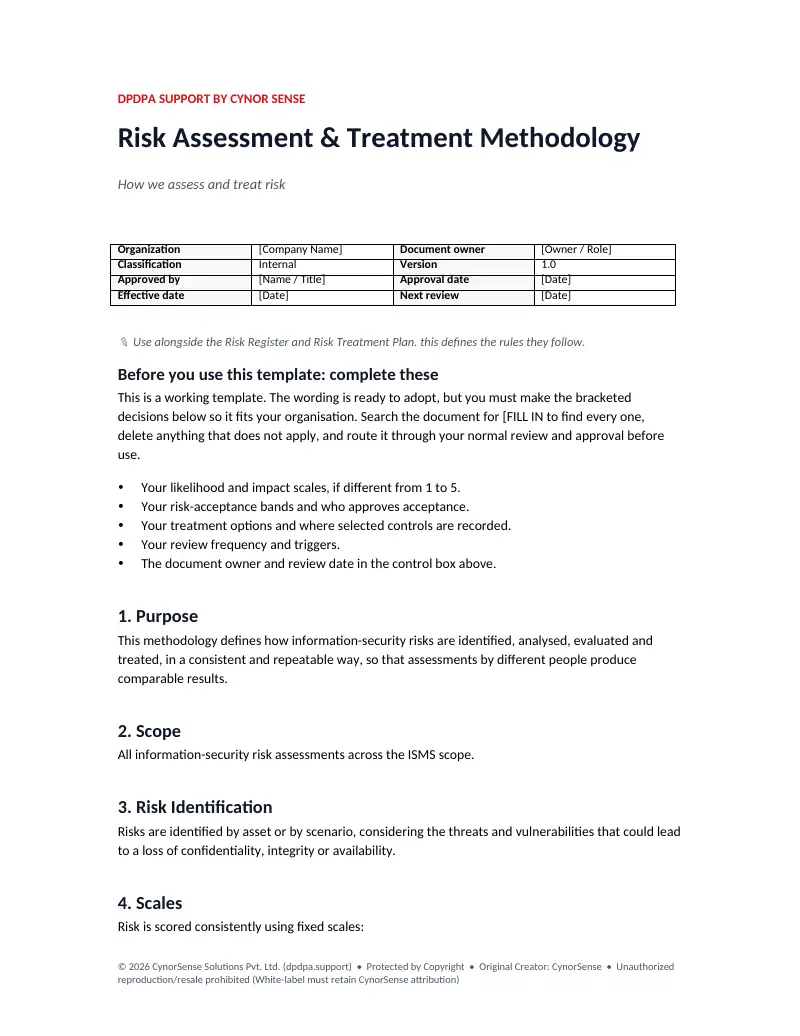 Risk Assessment Methodology
✎ Use alongside the Risk Register and Risk Treatment Plan.
-
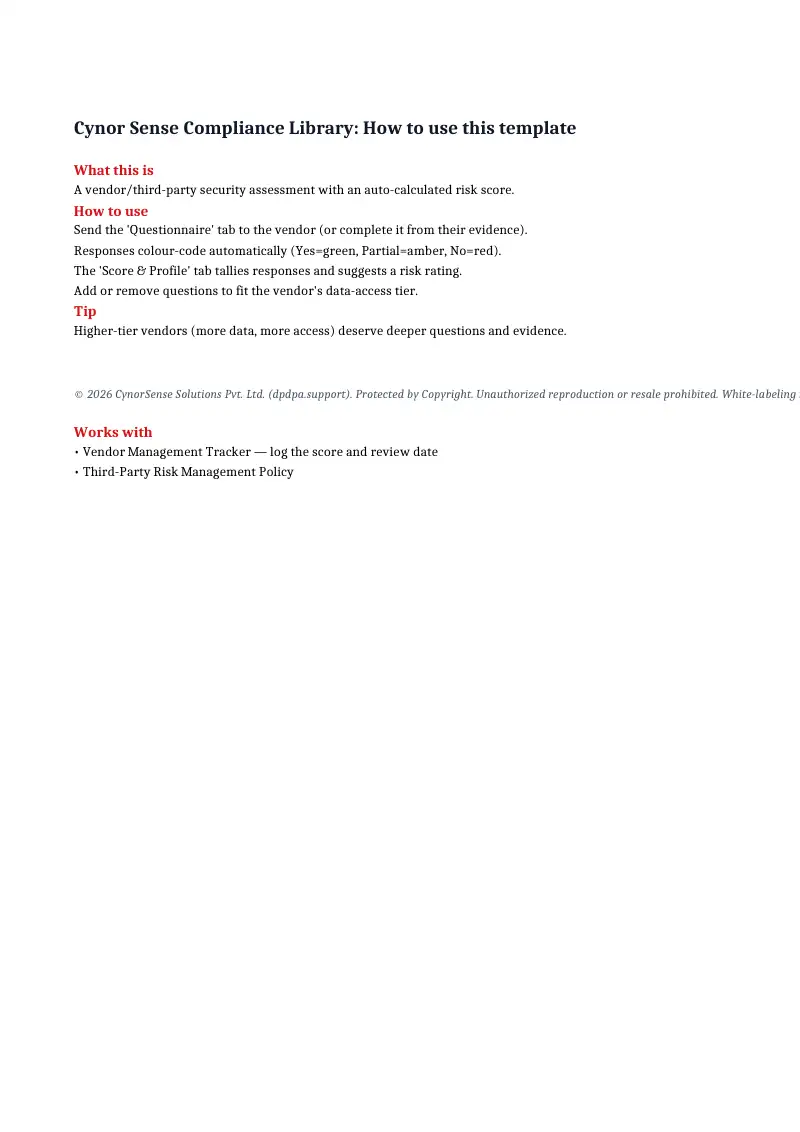 Vendor Risk Assessment
A vendor/third-party security assessment with an auto-calculated risk score.
Plans, procedures and forms5
-
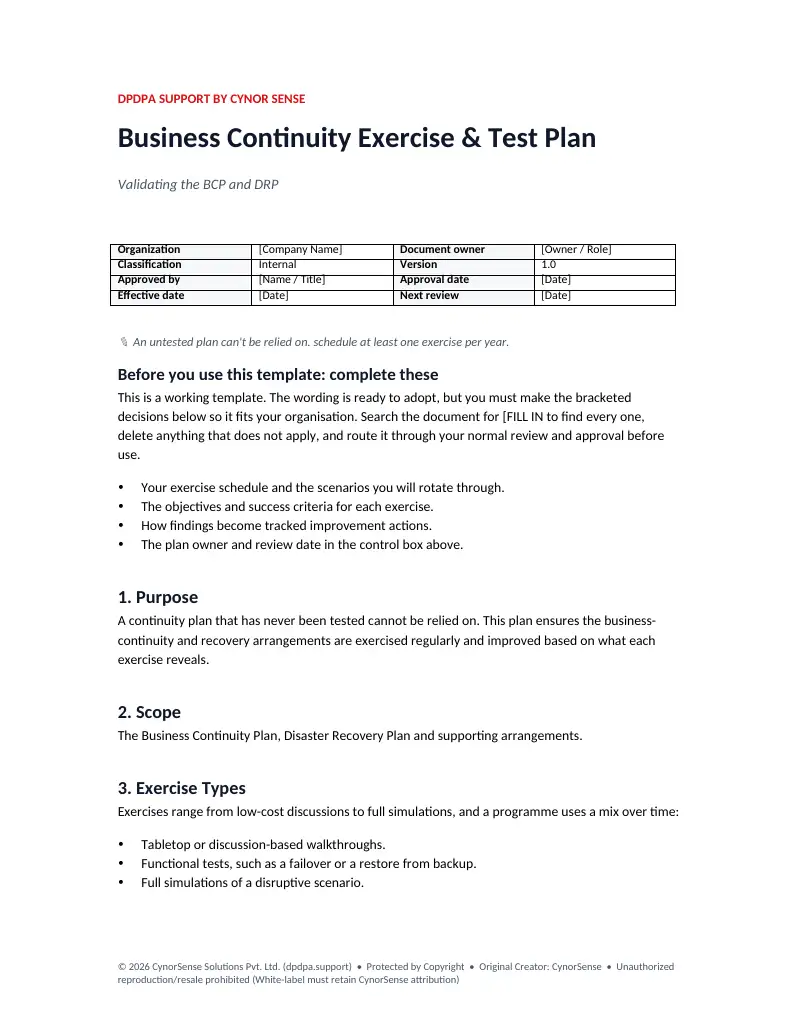 Business Continuity Exercise Test Plan
✎ An untested plan can't be relied on. schedule at least one exercise per year.
-
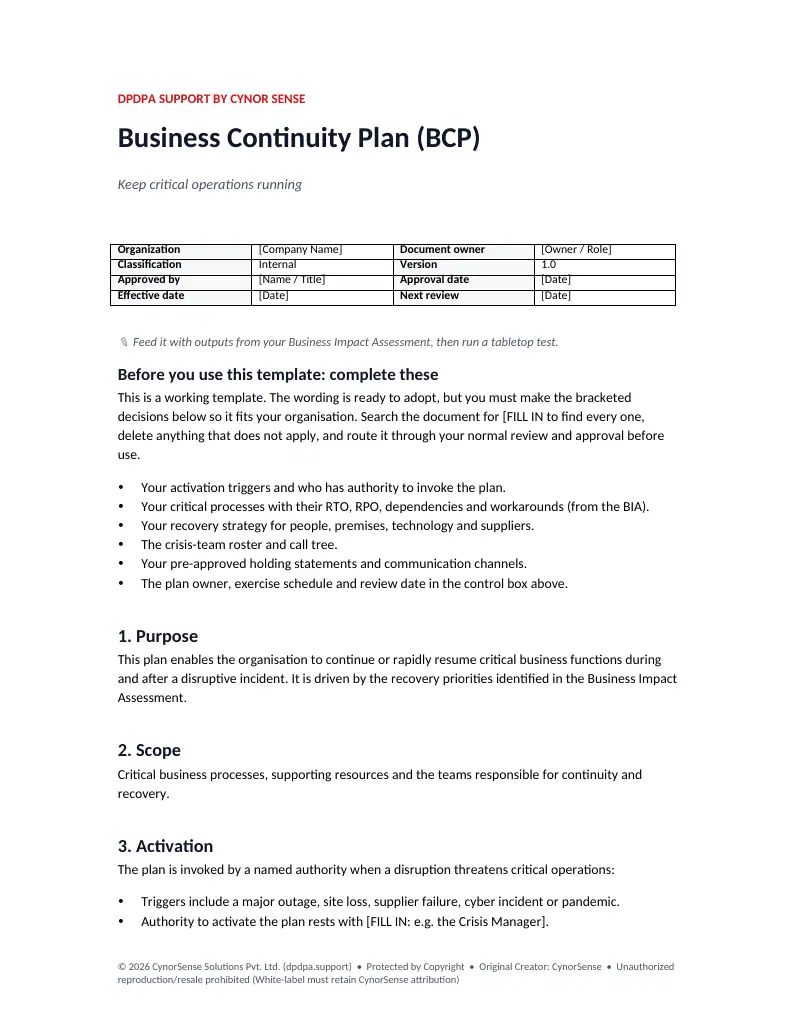 Business Continuity Plan
✎ Feed it with outputs from your Business Impact Assessment, then run a tabletop test.
-
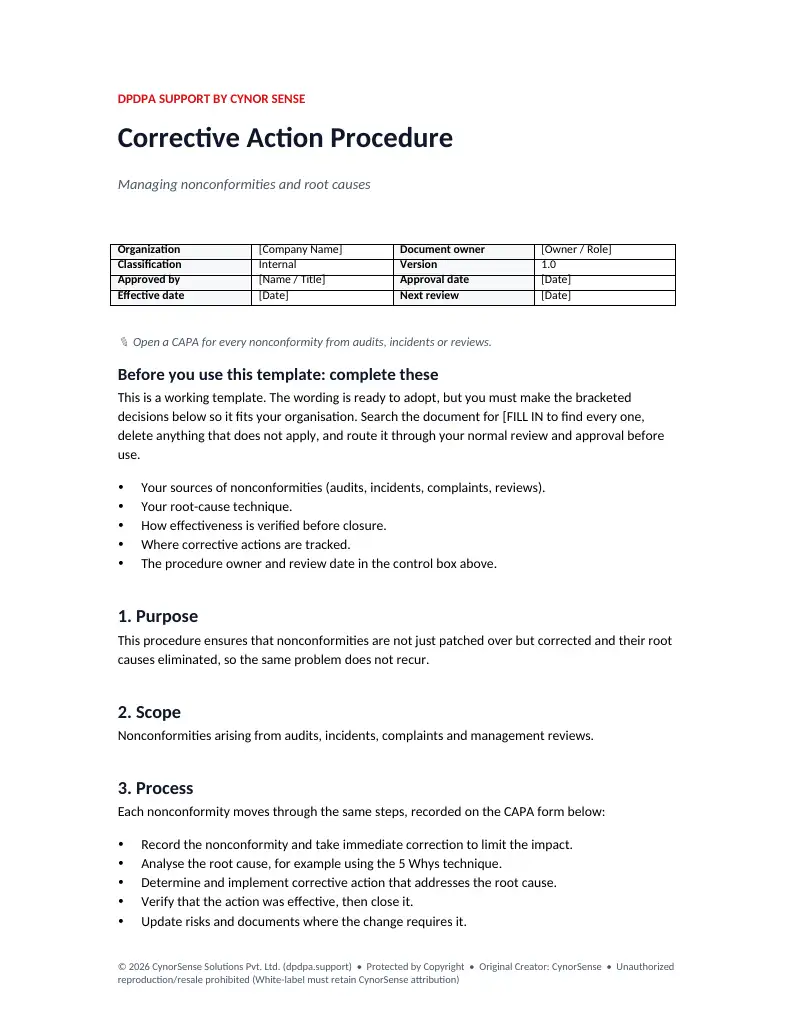 Corrective Action Capa Form
✎ Open a CAPA for every nonconformity from audits, incidents or reviews.
-
Cyber Incident Management Plan
This template serves as a basis for you to develop a basic cyber incident response plan (CIRP) for your organization.
-
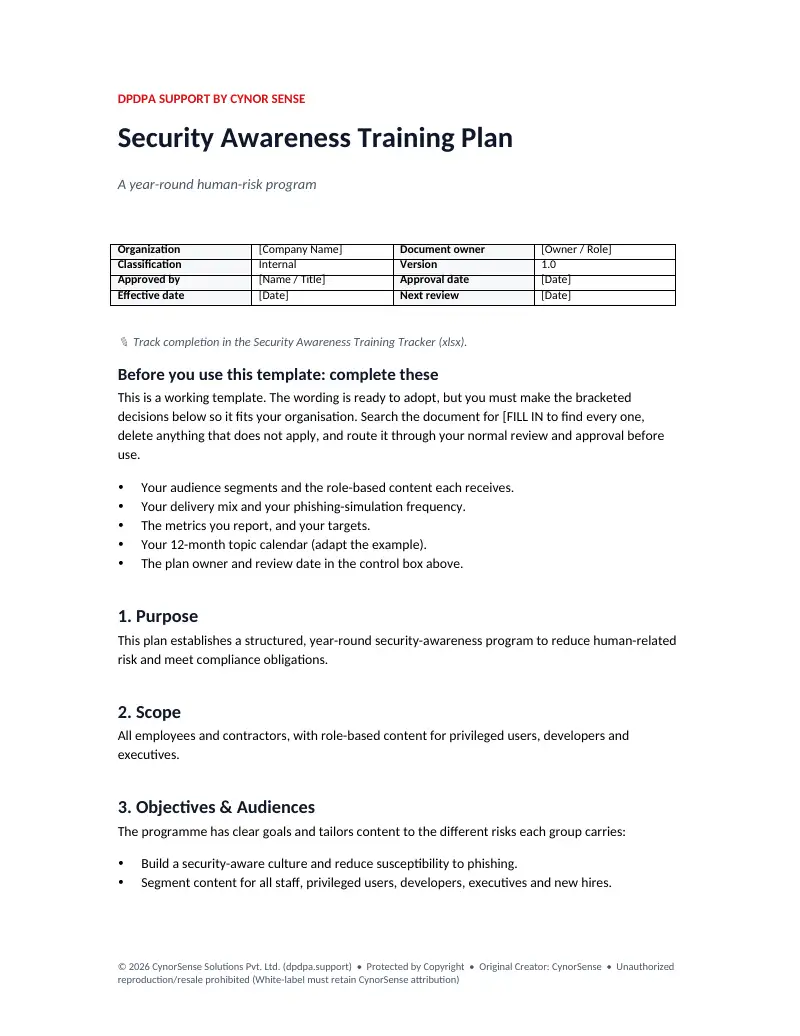 Security Awareness Training Plan
✎ Track completion in the Security Awareness Training Tracker (xlsx).
Policies and standards19
-
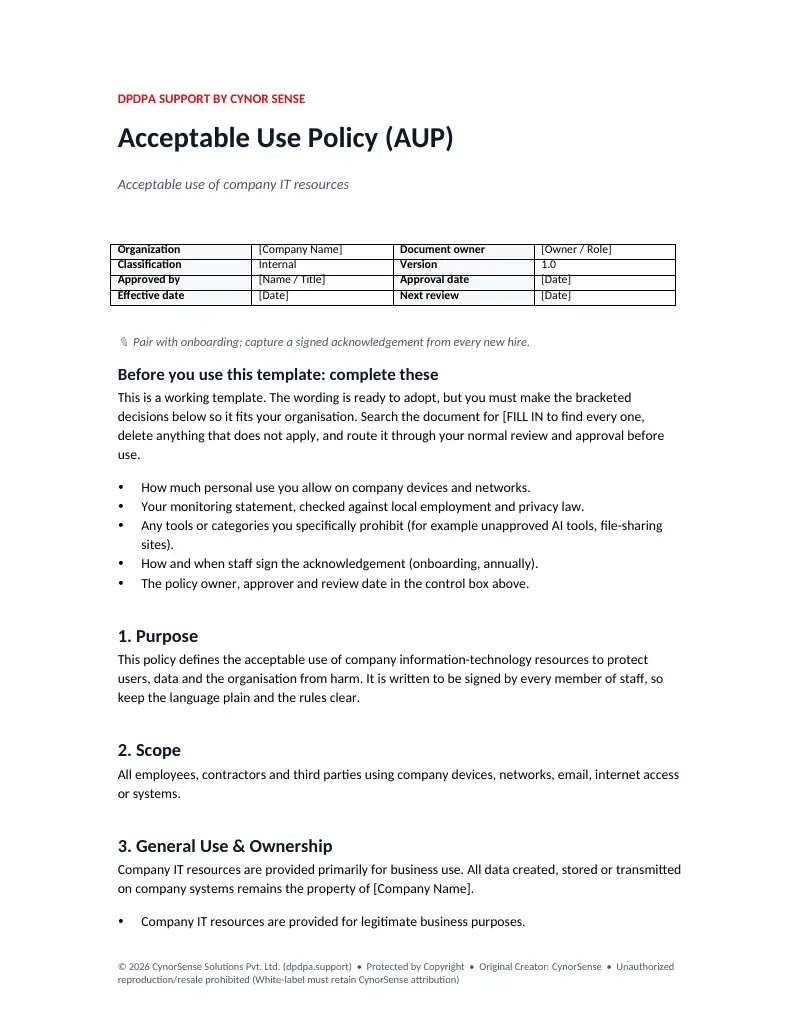 Acceptable Use Policy
✎ Pair with onboarding; capture a signed acknowledgement from every new hire.
-
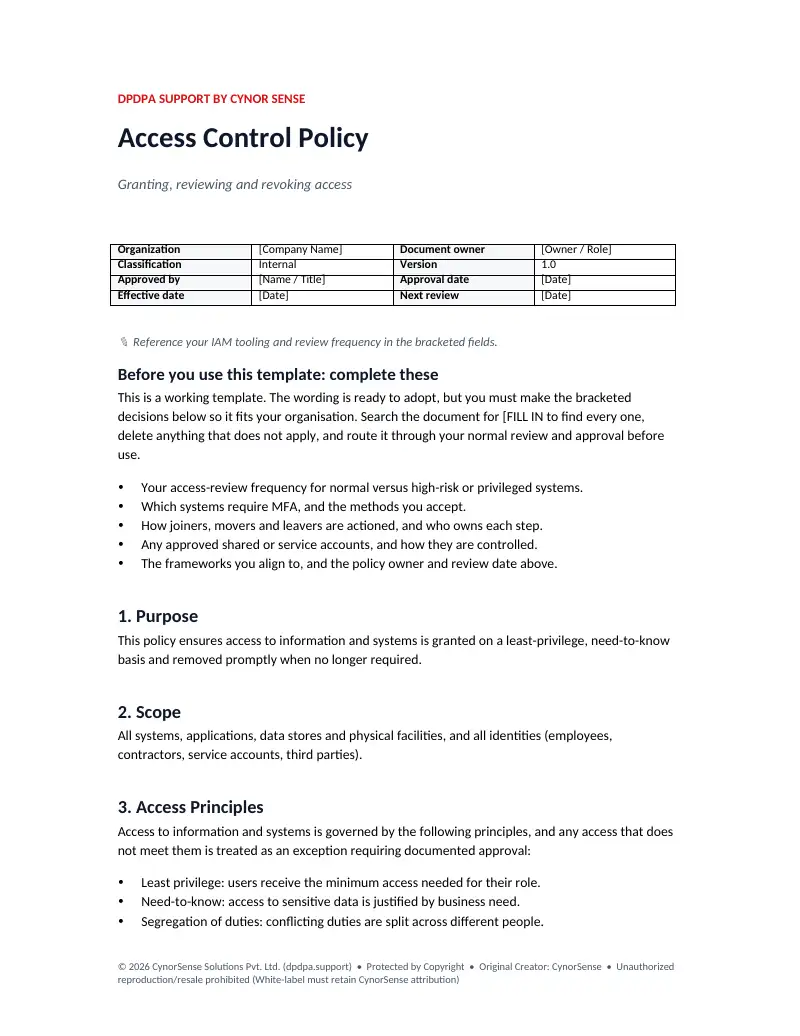 Access Control Policy
✎ Reference your IAM tooling and review frequency in the bracketed fields.
-
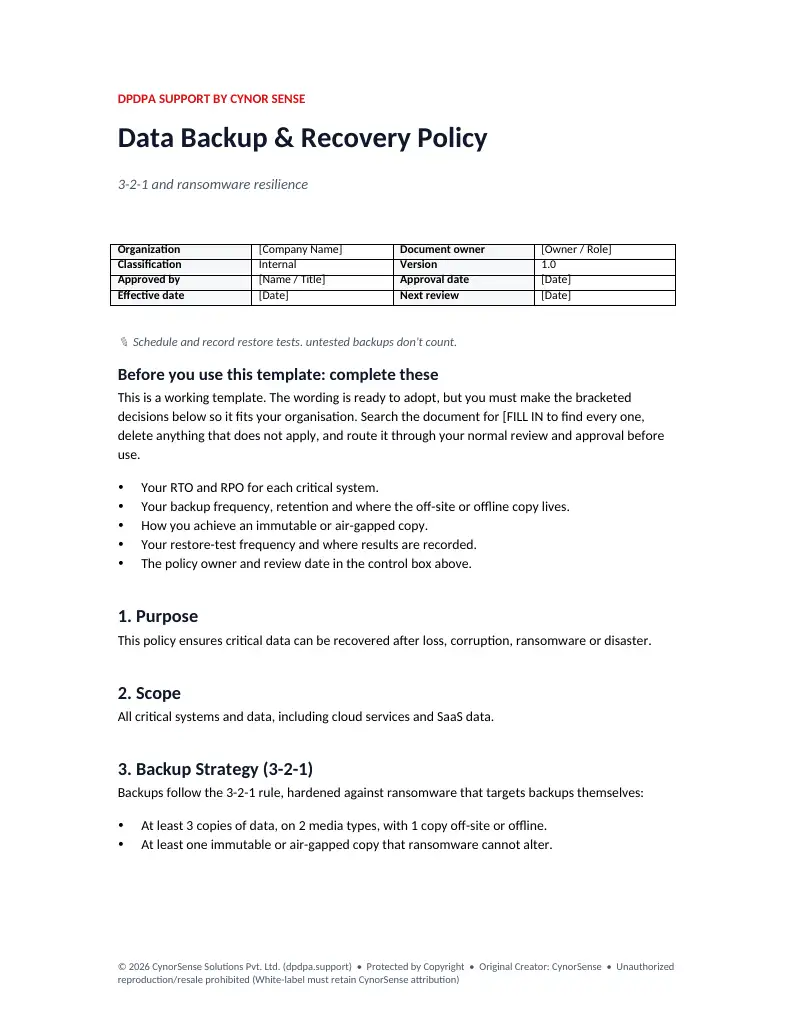 Backup Policy
✎ Schedule and record restore tests. untested backups don't count.
-
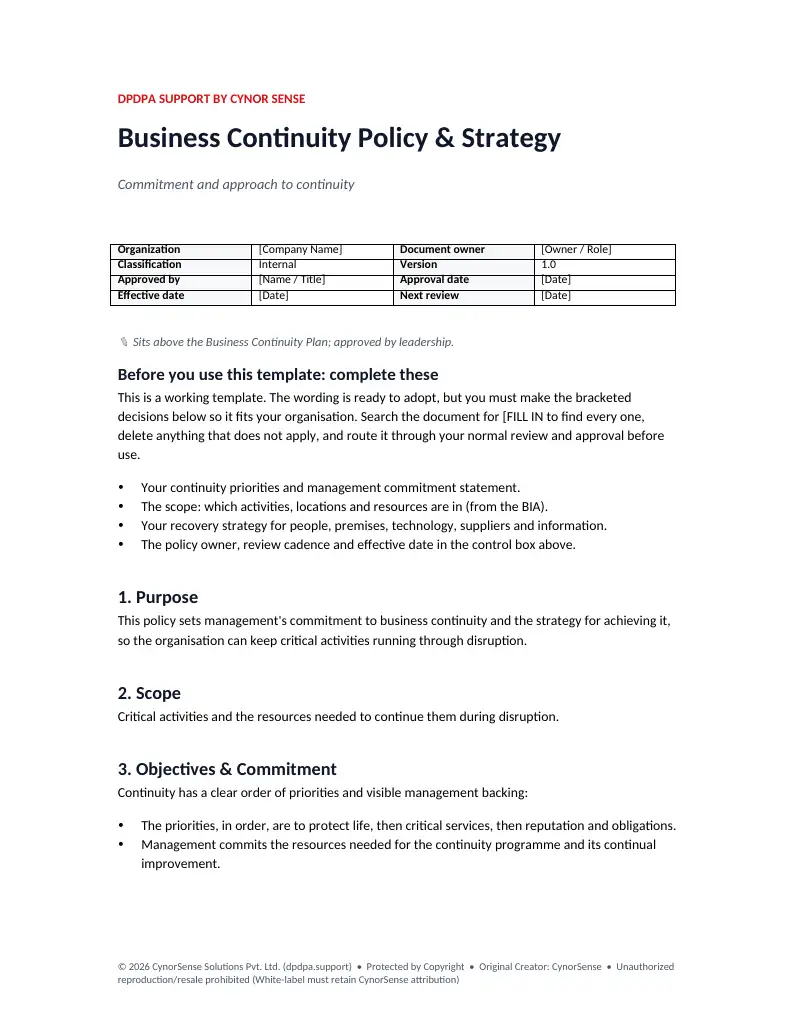 Business Continuity Policy
✎ Sits above the Business Continuity Plan; approved by leadership.
-
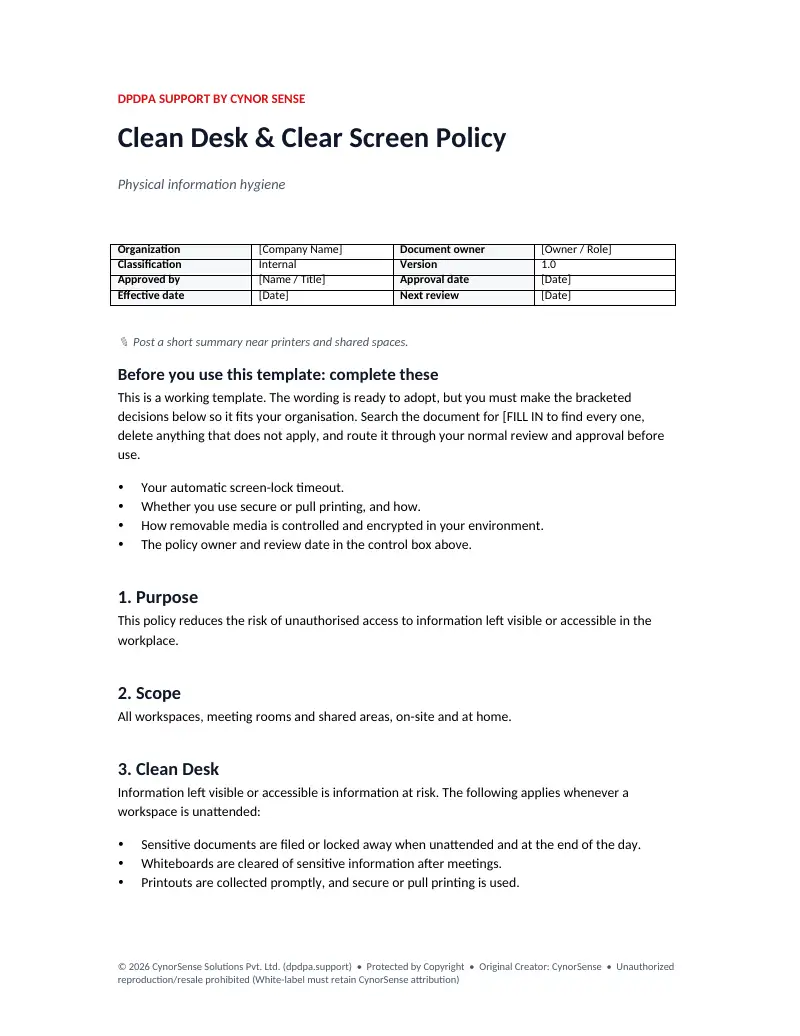
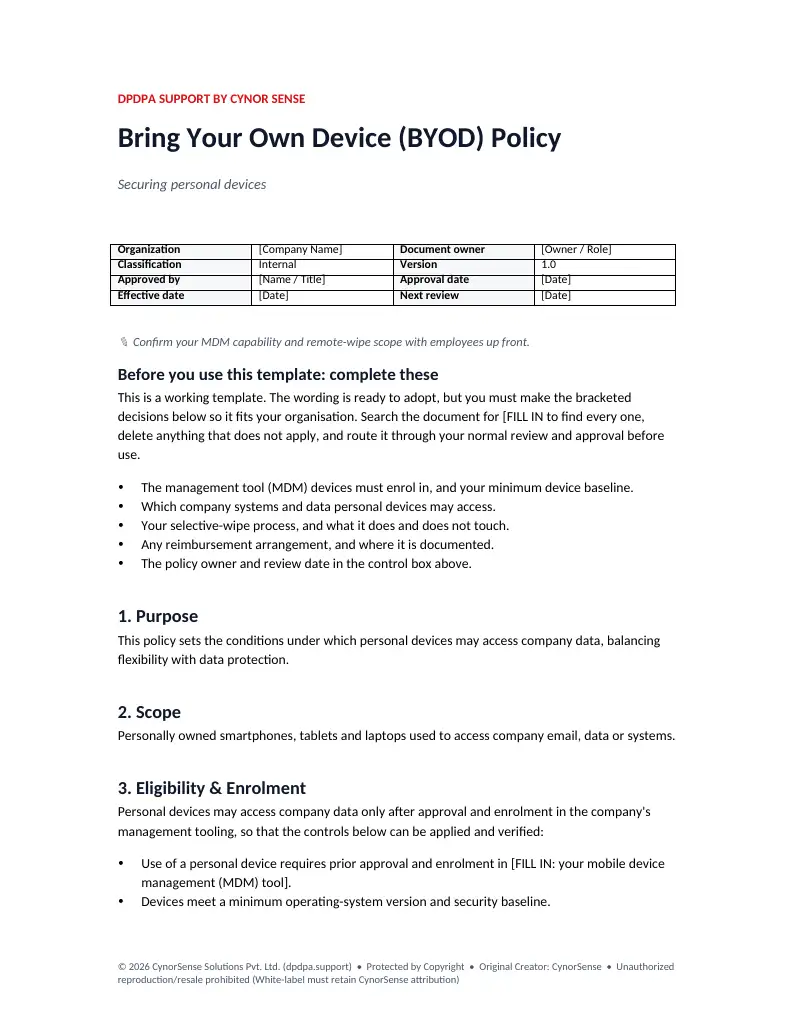 BYOD Policy
✎ Confirm your MDM capability and remote-wipe scope with employees up front.
-
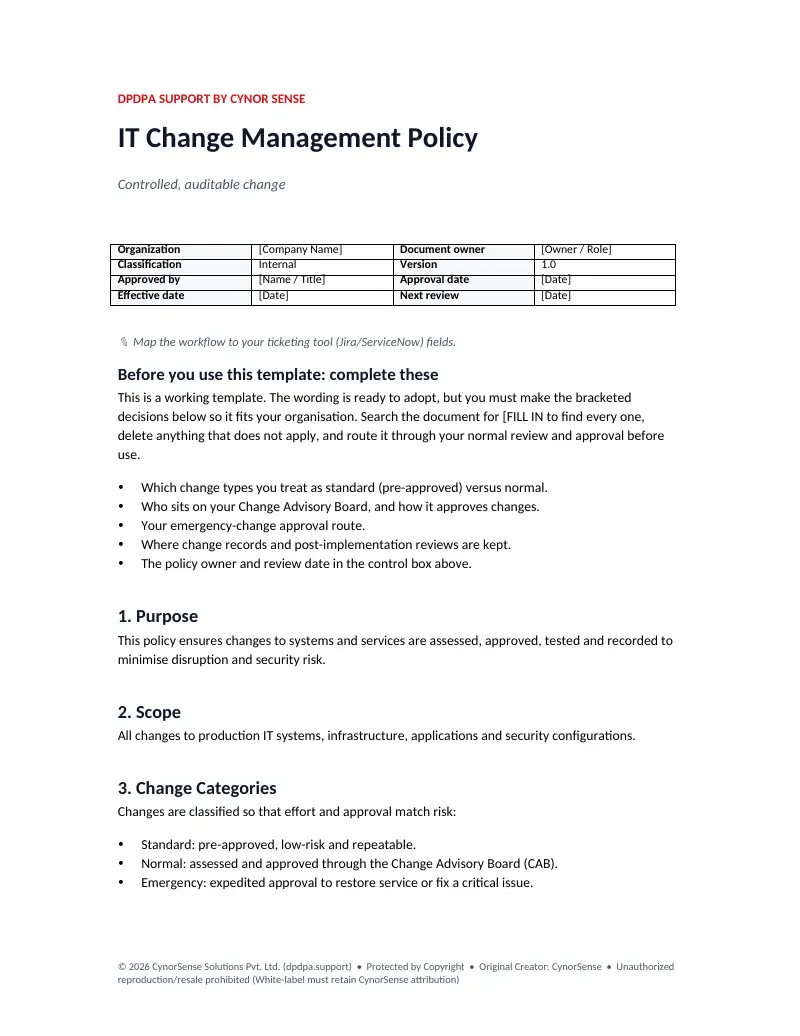 Change Management Policy
✎ Map the workflow to your ticketing tool (Jira/ServiceNow) fields.
-
-
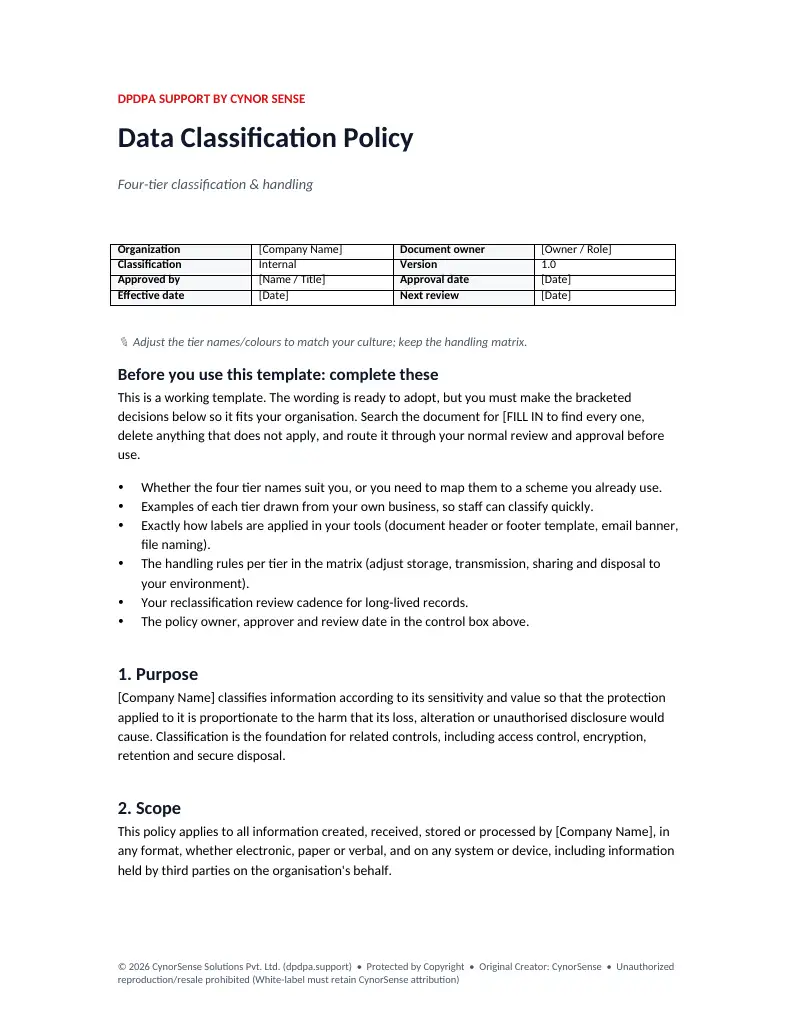 Data Classification Policy
✎ Adjust the tier names/colours to match your culture; keep the handling matrix.
-
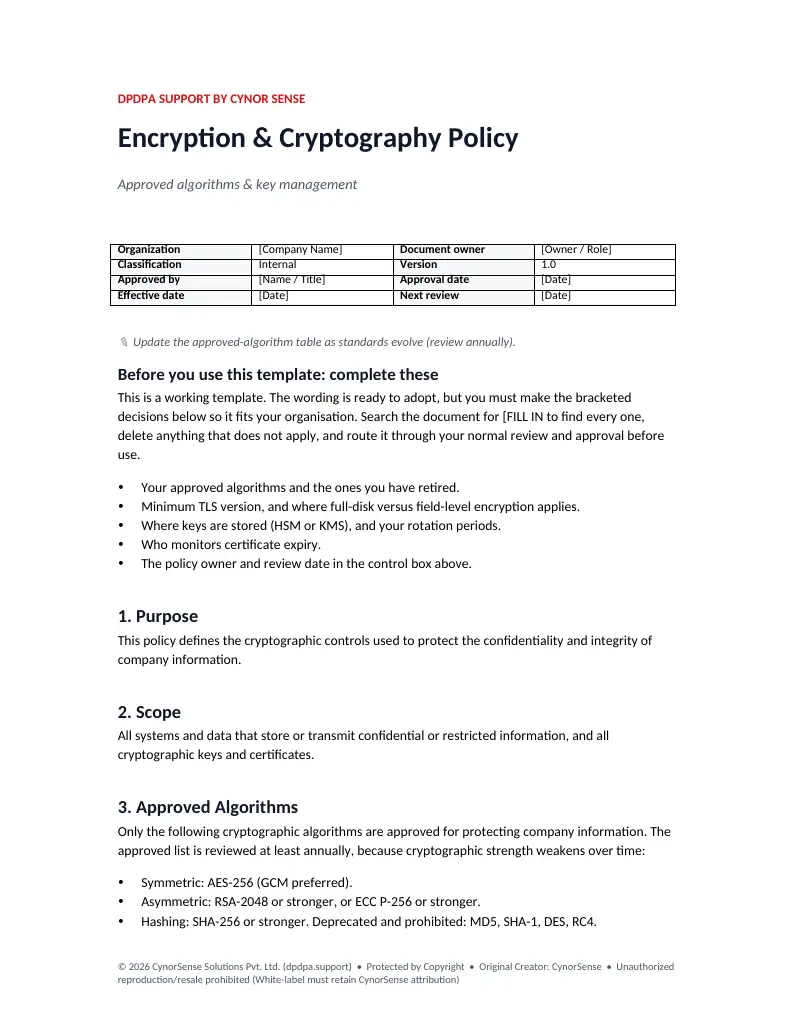 Encryption Policy
✎ Update the approved-algorithm table as standards evolve (review annually).
-
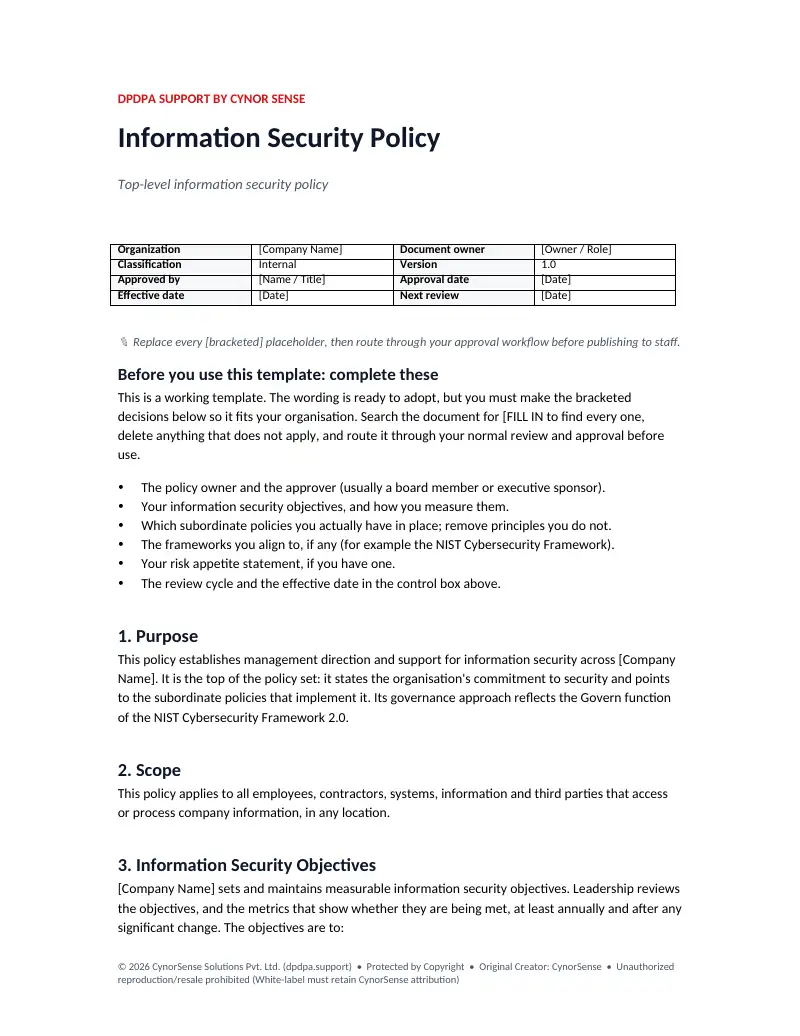 Information Security Policy
✎ Replace every [bracketed] placeholder, then route through your approval workflow before publishing to staff.
-
 Information Transfer Policy
✎ List your approved transfer channels and link to the data classification policy.
-
 Password Policy
✎ Set your minimum length and MFA scope in the bracketed fields before publishing.
-
 Patch Management Policy
✎ Set realistic SLAs you can actually meet, then measure against them.
-
 Physical Security Policy
✎ Tailor to each site; cloud-hosted infra inherits the provider's physical controls.
-
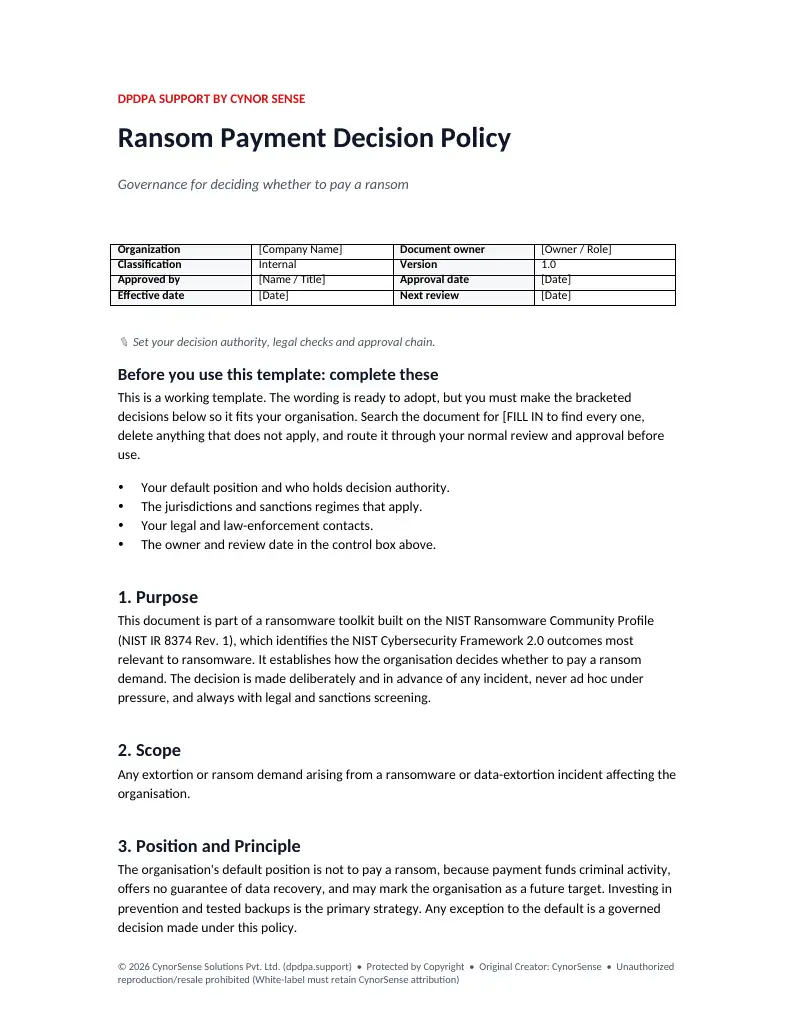
-
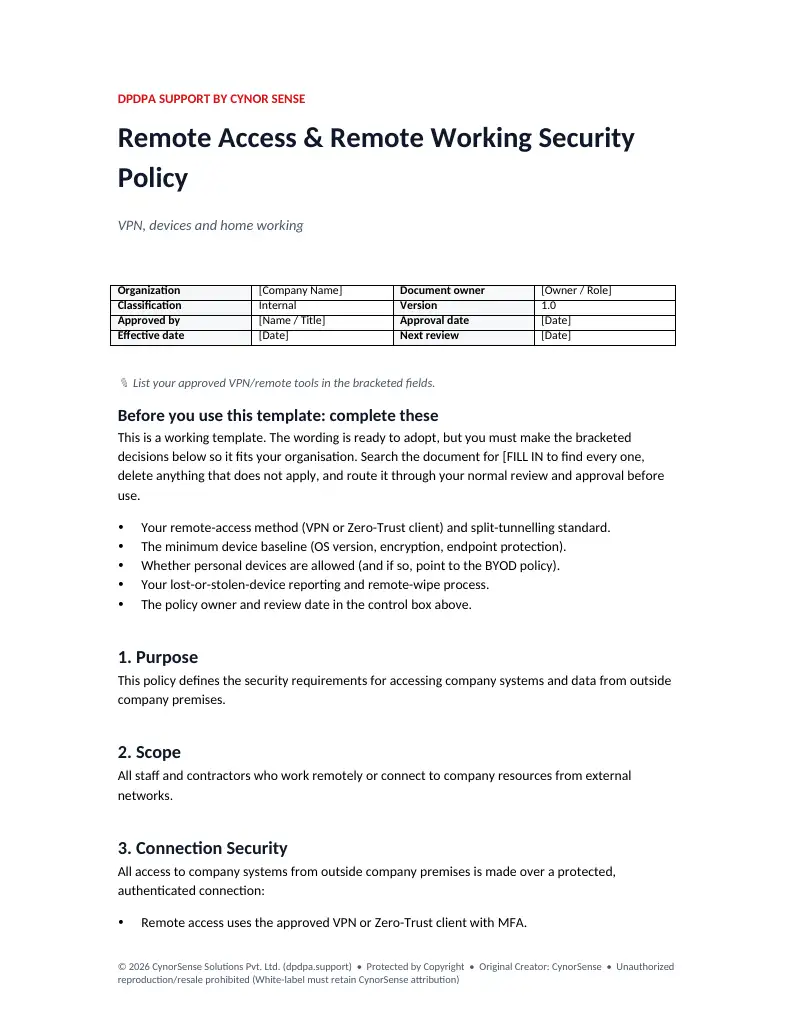
-
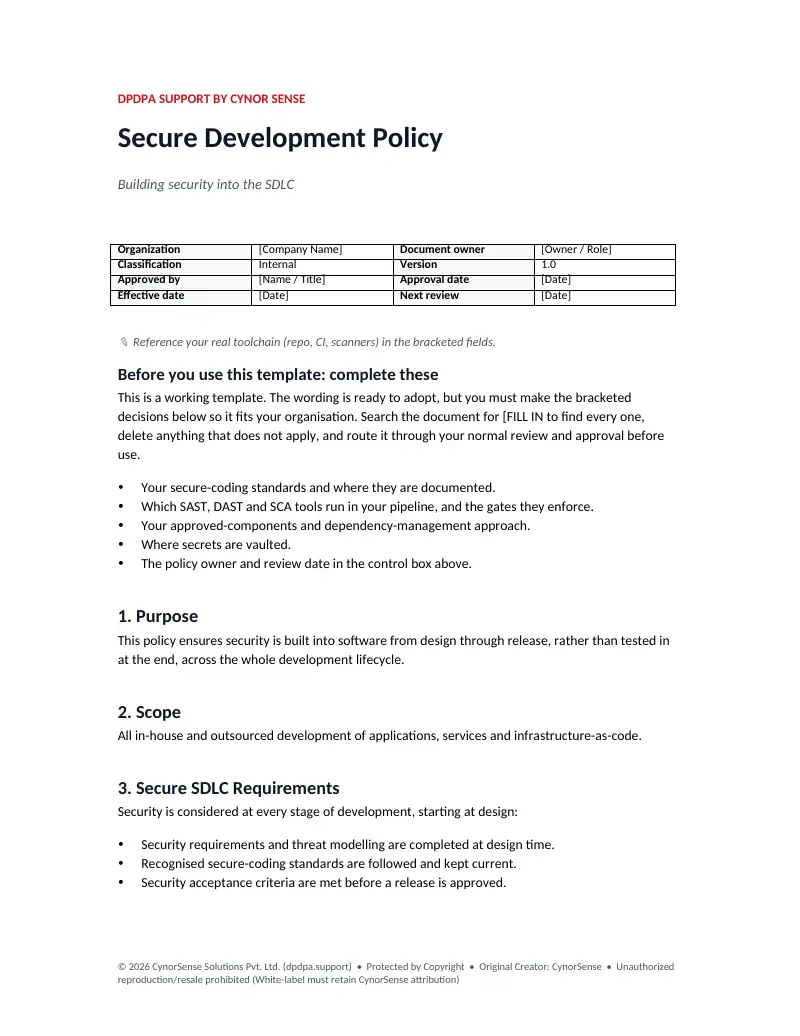 Secure Development Policy
✎ Reference your real toolchain (repo, CI, scanners) in the bracketed fields.
-
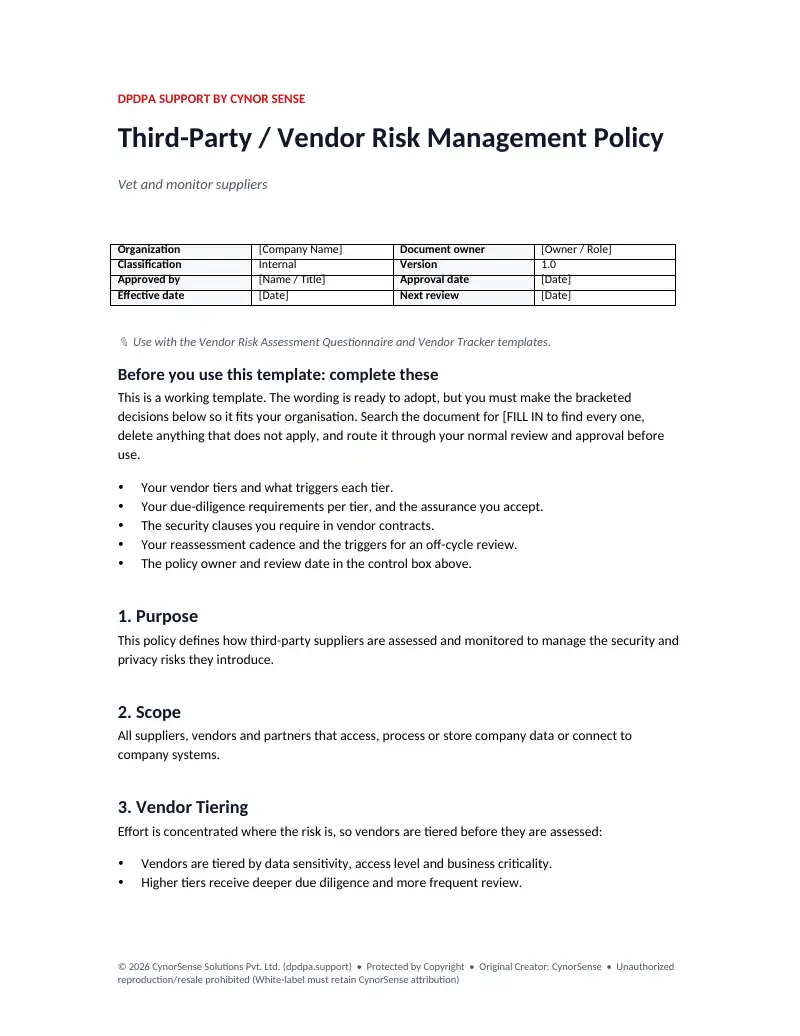 Third Party Risk Management Policy
✎ Use with the Vendor Risk Assessment Questionnaire and Vendor Tracker templates.
-
Briefings and other documents6
-
 Business Impact Analysis Bia
Formula-driven Excel register and assessment workbook (Cover, Instructions, Impact Assessment, Dashboard) structured for audit readiness, risk scoring, and executive…
-
 Cybersecurity Metrics Dashboard
A board-ready cybersecurity KPI dashboard with RAG status.
-
-
Monte Carlo Data Breach Cost Simulation
Formula-driven Excel register and assessment workbook (1 Guidance, 2 Baseline Settings, 3 Scenario & Mitigation Model, 4 - Consolidated Report) structured for audit…
-
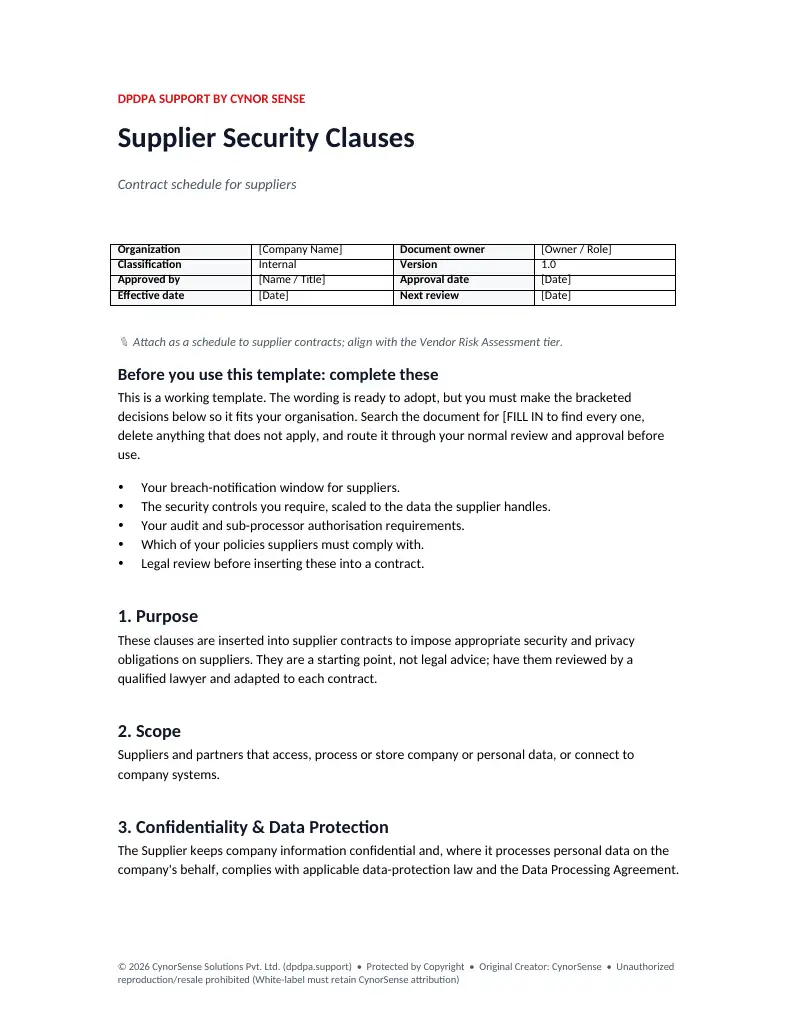 Supplier Security Clauses
✎ Attach as a schedule to supplier contracts; align with the Vendor Risk Assessment tier.
-
 User Access Review
A user access review (recertification) worksheet for SOC 2 / ISO 27001 evidence.
₹4,999 incl. GST
How the files fit together
A suggested order
Our suggestion, not a requirement of the standard or the law.
- 1
Find the gaps
Start with the assessment workbooks to see where you stand.
3 files: Employee Offboarding Security Checklist, Risk Assessment Methodology, Vendor Risk Assessment
- 2
Plan the work and the response
Use the plans, procedures and forms to set owners, dates and the steps to follow.
5 files: Business Continuity Exercise Test Plan, Business Continuity Plan, Corrective Action Capa Form, Cyber Incident Management Plan and more
- 3
Approve the policies
Edit the policies to match how you work, then get them approved.
19 files: Acceptable Use Policy, Access Control Policy, Backup Policy, Business Continuity Policy and more
- 4
Keep the records
Keep the registers and logs up to date as evidence for an audit or a review.
11 files: Data Breach Register, Document and Record Control Procedure, It Asset Inventory, Legal and Regulatory Requirements Register and more
- 5
Brief your leadership
Use the briefing documents to explain the work to decision makers.
6 files: Business Impact Analysis Bia, Cybersecurity Metrics Dashboard, Management Review Meeting, Monte Carlo Data Breach Cost Simulation and more
Questions
Before you buy
What exactly do I get?
44 editable files (28 Word, 16 Excel). Every file is listed on this page with its file name, size and number of sections.
How are the files delivered?
Digitally, after your payment is confirmed: we email download links to the address you gave at checkout. Each link works for 2 hours; you can ask for a fresh one from My purchases. Nothing is shipped.
How do I pay?
Through Razorpay, by UPI, card or netbanking.
Is GST included?
Yes. The price includes GST. To get a GST invoice, email [email protected] with your billing name, address and GSTIN.
Are these official documents of the standard body or regulator?
No. They are templates supplied by CynorSense Solutions Pvt. Ltd. They are not issued or endorsed by any standard body or regulator, and they are not legal advice. Using them does not by itself make an organisation compliant or certified.