

Framework toolkit
EU DORA Financial ICT Risk & Third-Party Resilience Toolkit
11 editable templates: 6 Excel, 5 Word. Each one is listed below with page 1 and its sections.
₹9,999 incl. GST
Review cart (0)- 11 files you can edit in Word and Excel
- UPI, card or netbanking through Razorpay
Three of the 11. Open one to see its full outline.
What you get
All 11 files in this toolkit
Registers, logs and trackers3
-
 DORA Ict Incident Register
A register of ICT-related incidents under DORA (Regulation (EU) 2022/2554), with classification of major incidents (Art.
-
 DORA Register of Information
The register of information on all contractual arrangements for the use of ICT services provided by ICT third-party service providers, which DORA requires financial…
-
Assessments and checklists2
-
 DORA Gap Assessment
A gap assessment against the Digital Operational Resilience Act (Regulation (EU) 2022/2554): governance and ICT risk management (Art.
-
Plans, procedures and forms3
-
 DORA Compliance Roadmap
A roadmap to drive your DORA gap assessment into a prioritised, owned action plan.
-
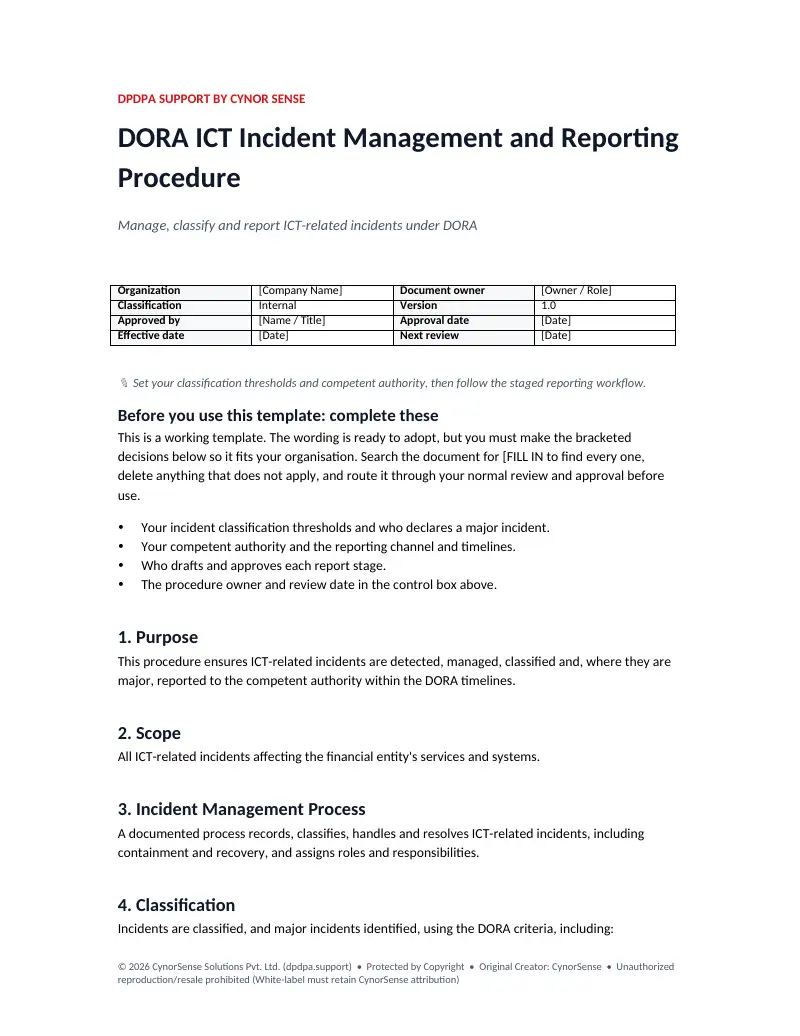 DORA Ict Incident Management Procedure
✎ Set your classification thresholds and competent authority, then follow the staged reporting workflow.
-
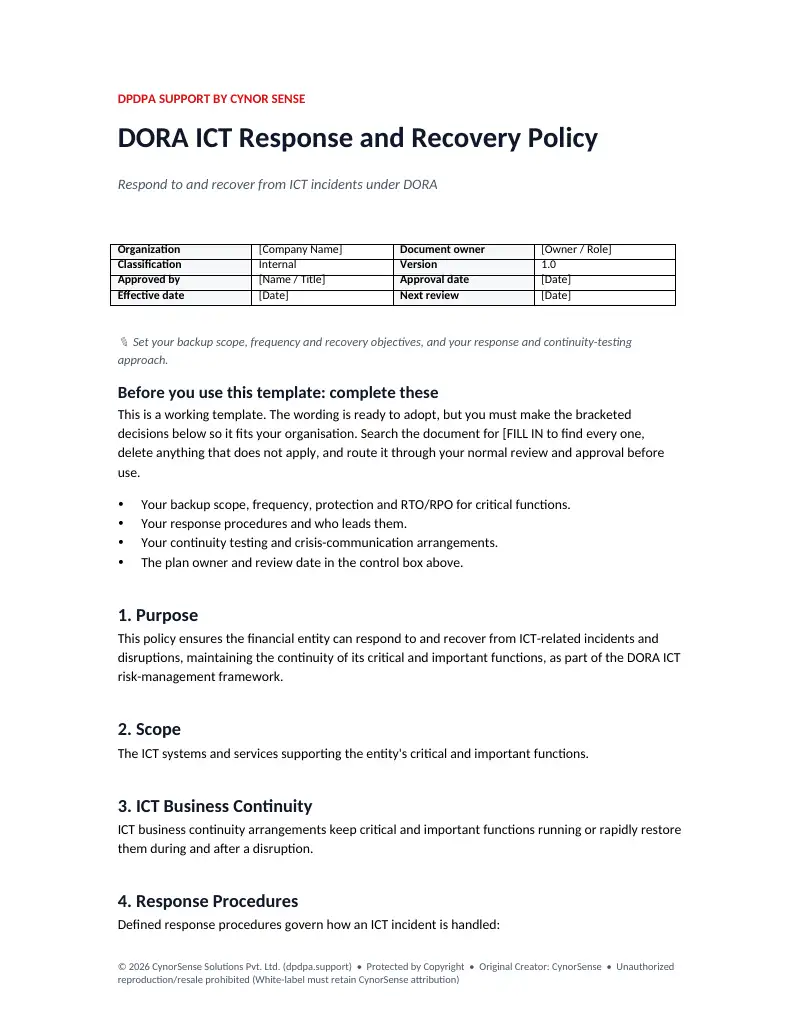 DORA Ict Response Recovery Policy
✎ Set your backup scope, frequency and recovery objectives, and your response and continuity-testing approach.
Policies and standards3
-
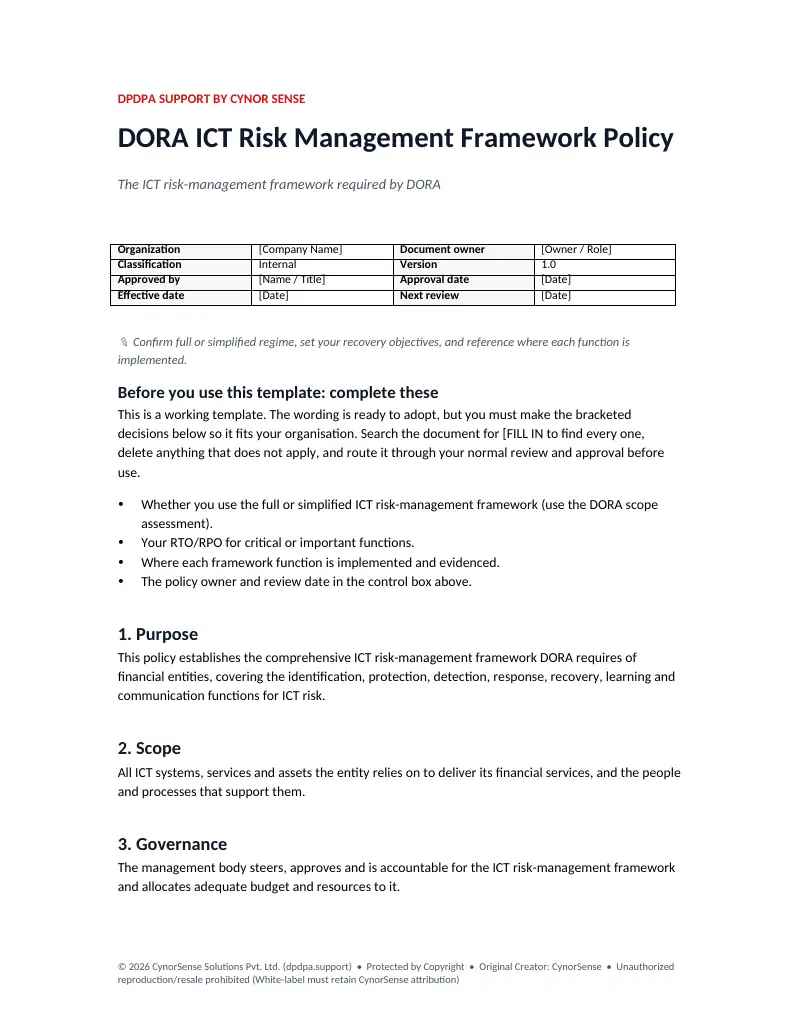 DORA Ict Risk Management Framework Policy
✎ Confirm full or simplified regime, set your recovery objectives, and reference where each function is implemented.
-
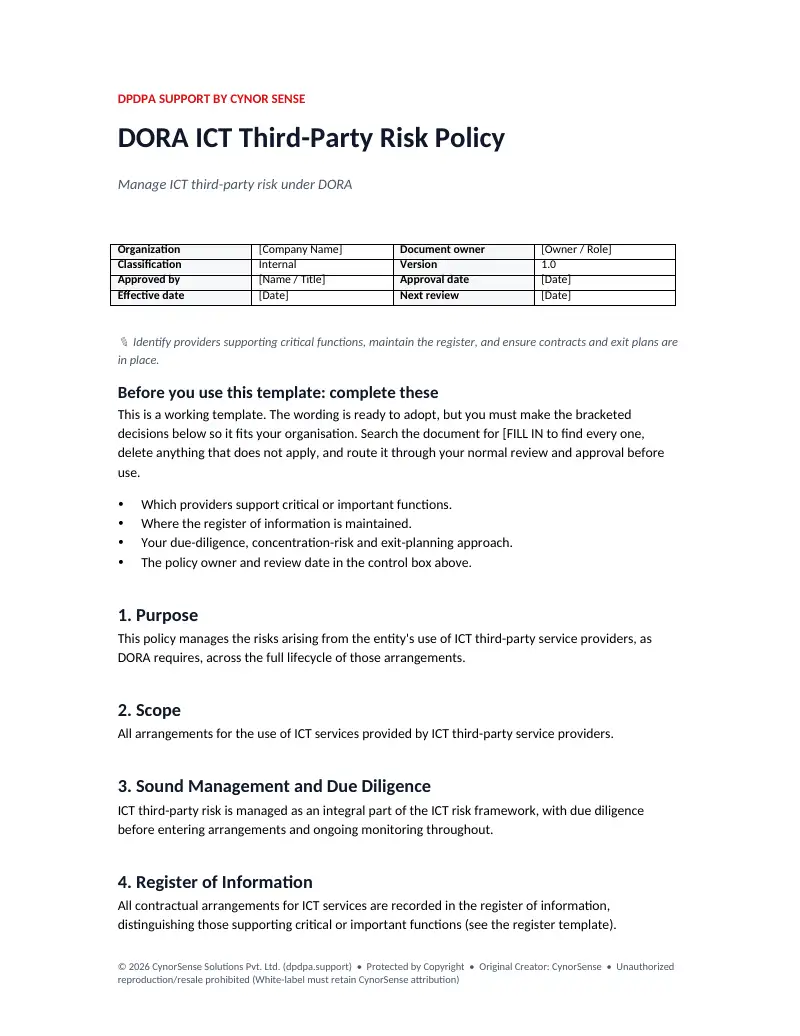 DORA Ict Third Party Risk Policy
✎ Identify providers supporting critical functions, maintain the register, and ensure contracts and exit plans are in place.
-
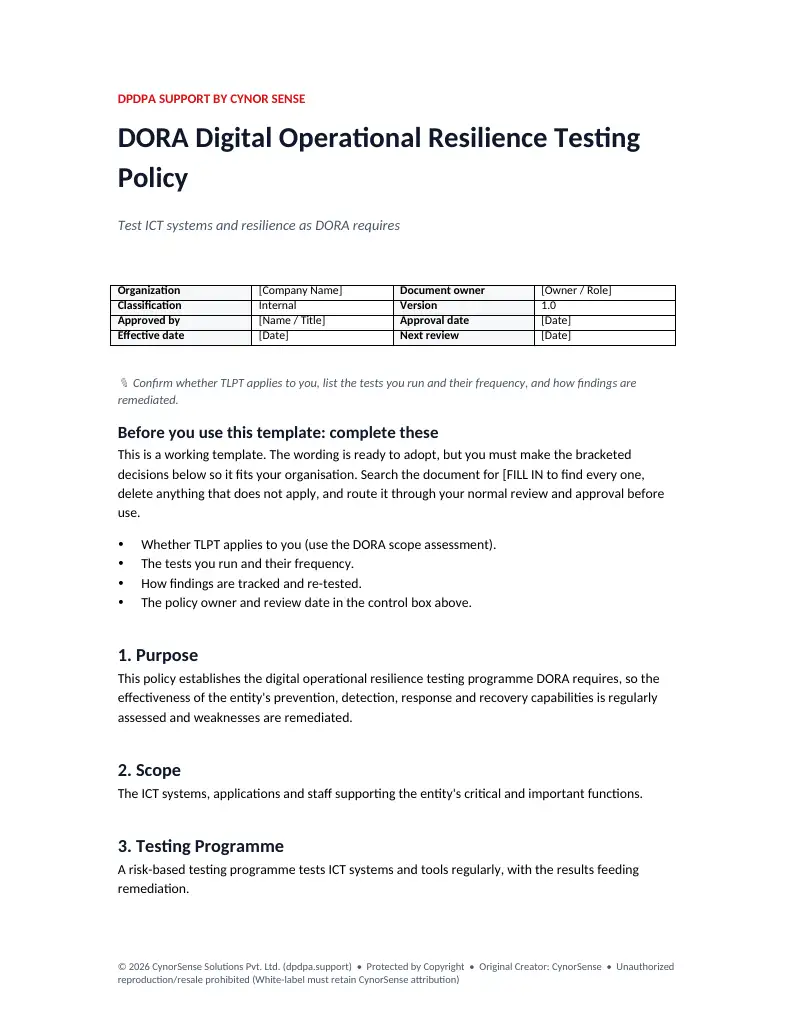 DORA Resilience Testing Policy
✎ Confirm whether TLPT applies to you, list the tests you run and their frequency, and how findings are remediated.
₹9,999 incl. GST
How the files fit together
A suggested order
Our suggestion, not a requirement of the standard or the law.
- 1
Find the gaps
Start with the assessment workbooks to see where you stand.
2 files: DORA Gap Assessment, DORA Ict Contractual Requirements Checklist
- 2
Plan the work and the response
Use the plans, procedures and forms to set owners, dates and the steps to follow.
3 files: DORA Compliance Roadmap, DORA Ict Incident Management Procedure, DORA Ict Response Recovery Policy
- 3
Approve the policies
Edit the policies to match how you work, then get them approved.
3 files: DORA Ict Risk Management Framework Policy, DORA Ict Third Party Risk Policy, DORA Resilience Testing Policy
- 4
Keep the records
Keep the registers and logs up to date as evidence for an audit or a review.
3 files: DORA Ict Incident Register, DORA Register of Information, DORA Scope Applicability Assessment
Questions
Before you buy
What exactly do I get?
11 editable files (6 Excel, 5 Word). Every file is listed on this page with its file name, size and number of sections.
How are the files delivered?
Digitally, after your payment is confirmed: we email download links to the address you gave at checkout. Each link works for 2 hours; you can ask for a fresh one from My purchases. Nothing is shipped.
How do I pay?
Through Razorpay, by UPI, card or netbanking.
Is GST included?
Yes. The price includes GST. To get a GST invoice, email [email protected] with your billing name, address and GSTIN.
Are these official documents of the standard body or regulator?
No. They are templates supplied by CynorSense Solutions Pvt. Ltd. They are not issued or endorsed by any standard body or regulator, and they are not legal advice. Using them does not by itself make an organisation compliant or certified.