

Framework toolkit
ISO/IEC 27017 Cloud Security & 27018 Cloud PII Toolkit
9 editable templates: 7 Word, 2 Excel. Each one is listed below with page 1 and its sections.
₹5,999 incl. GST
Review cart (0)- 9 files you can edit in Word and Excel
- UPI, card or netbanking through Razorpay
Three of the 9. Open one to see its full outline.
 Word38 KB
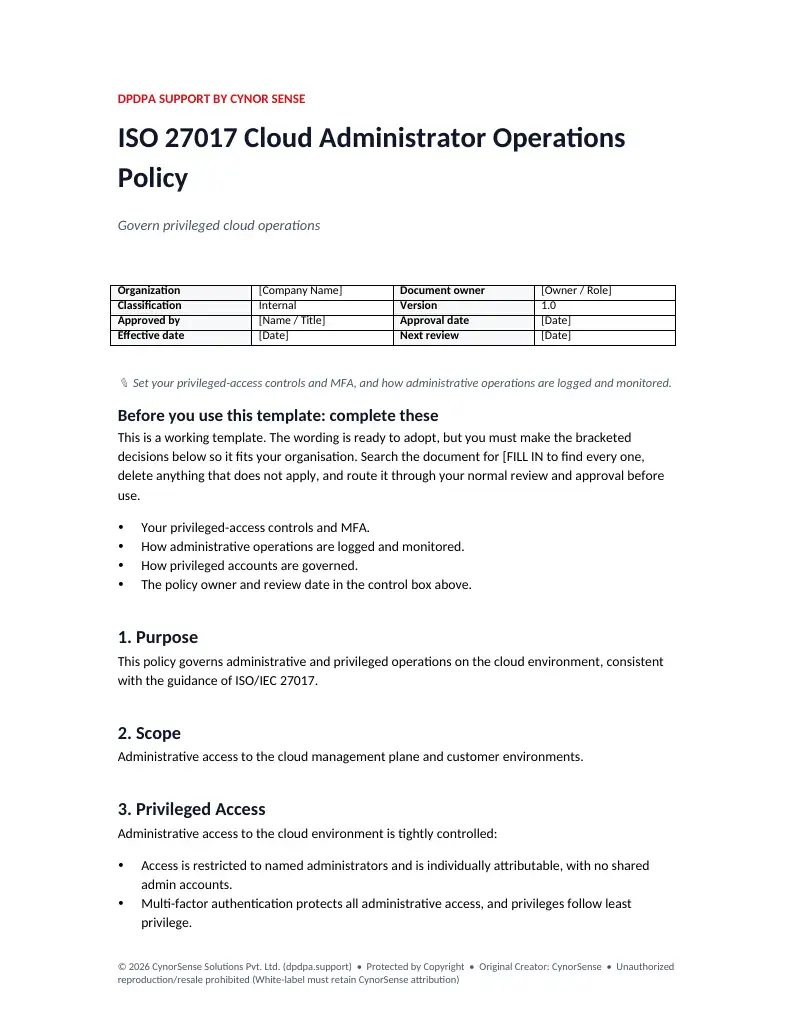
ISO 27017 Cloud Administrator Operations Policy
- 1. Purpose
- 2. Scope
- 3. Privileged Access
- 4. Logging and Monitoring
- + 4 more
 Excel9 KB
ISO 27017 Cloud Security Gap Assessment
- ISO 27017 Gap
- Summary
 Word38 KB
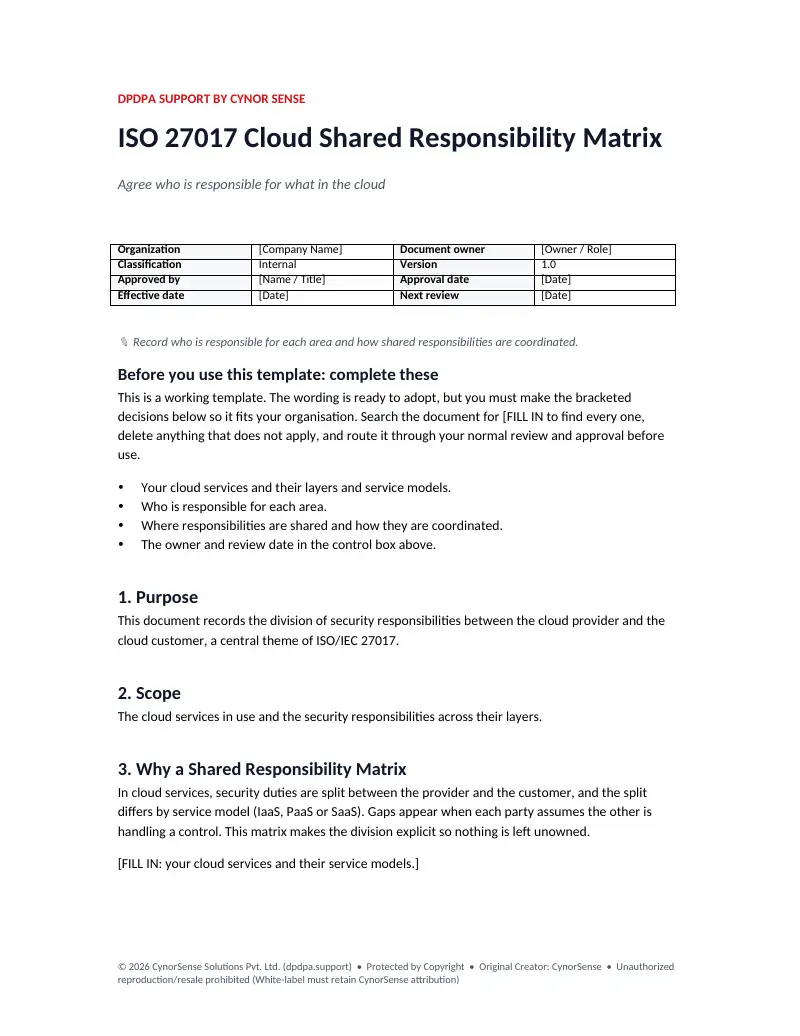
ISO 27017 Cloud Shared Responsibility Matrix
- 1. Purpose
- 2. Scope
- 3. Why a Shared Responsibility Matrix
- 4. Responsibility Matrix
- + 4 more
What you get
All 9 files in this toolkit
Registers, logs and trackers1
-
ISO 27017 Cloud Shared Responsibility Matrix
✎ Record who is responsible for each area and how shared responsibilities are coordinated.
Assessments and checklists2
-
ISO 27017 Cloud Security Gap Assessment
A gap assessment against the cloud security guidance of ISO/IEC 27017, which adds cloud-specific guidance on top of an ISO 27001 / 27002 control set, for both cloud…
-
 ISO 27018 Cloud Privacy Gap Assessment
A gap assessment against the cloud privacy guidance of ISO/IEC 27018, for protecting personally identifiable information (PII) in public clouds acting as a PII processor.
Policies and standards6
-
ISO 27017 Cloud Administrator Operations Policy
✎ Set your privileged-access controls and MFA, and how administrative operations are logged and monitored.
-
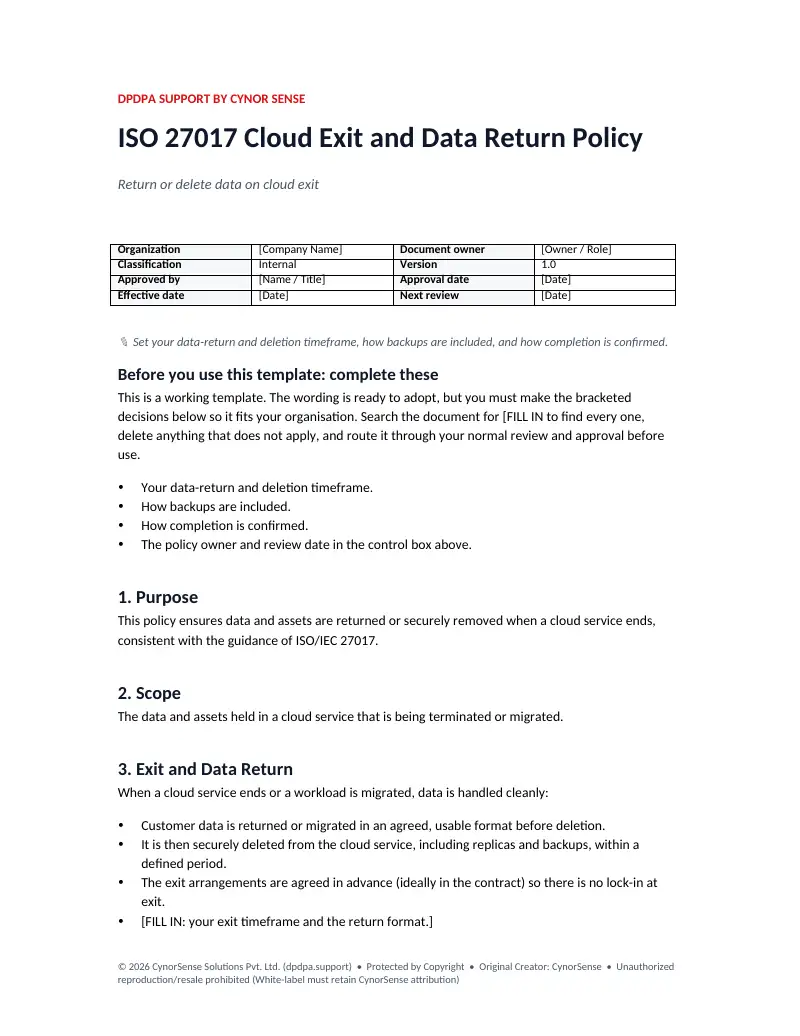 ISO 27017 Cloud Exit Data Return Policy
✎ Set your data-return and deletion timeframe, how backups are included, and how completion is confirmed.
-
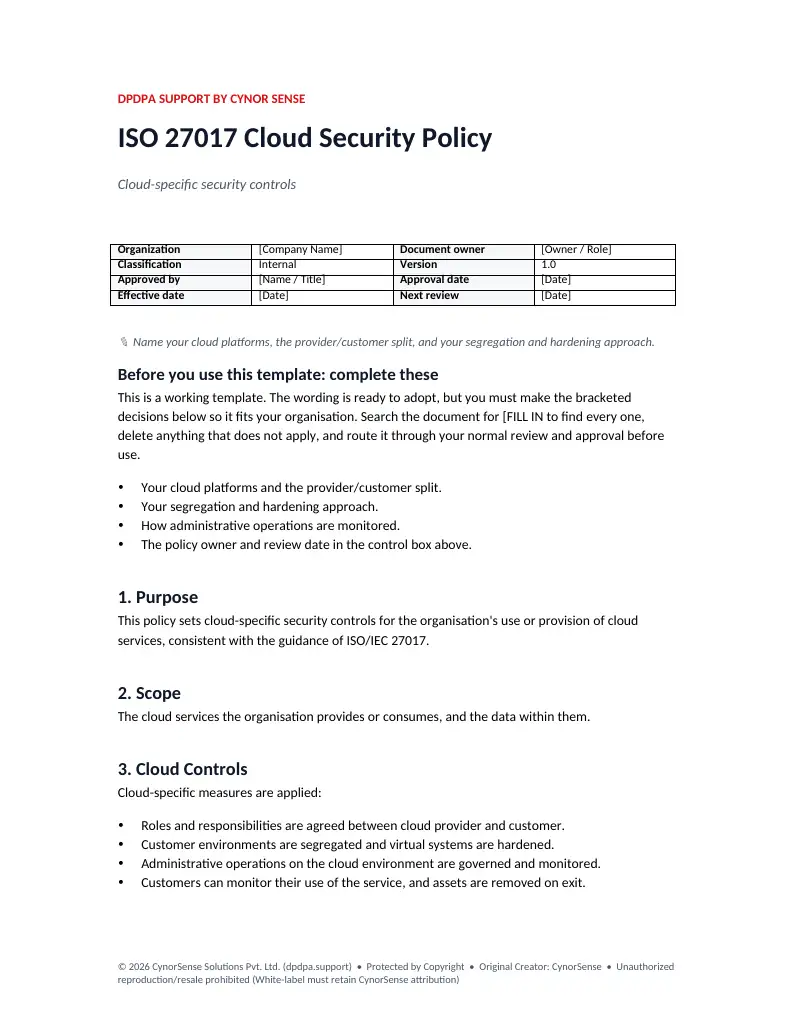 ISO 27017 Cloud Security Policy
✎ Name your cloud platforms, the provider/customer split, and your segregation and hardening approach.
-
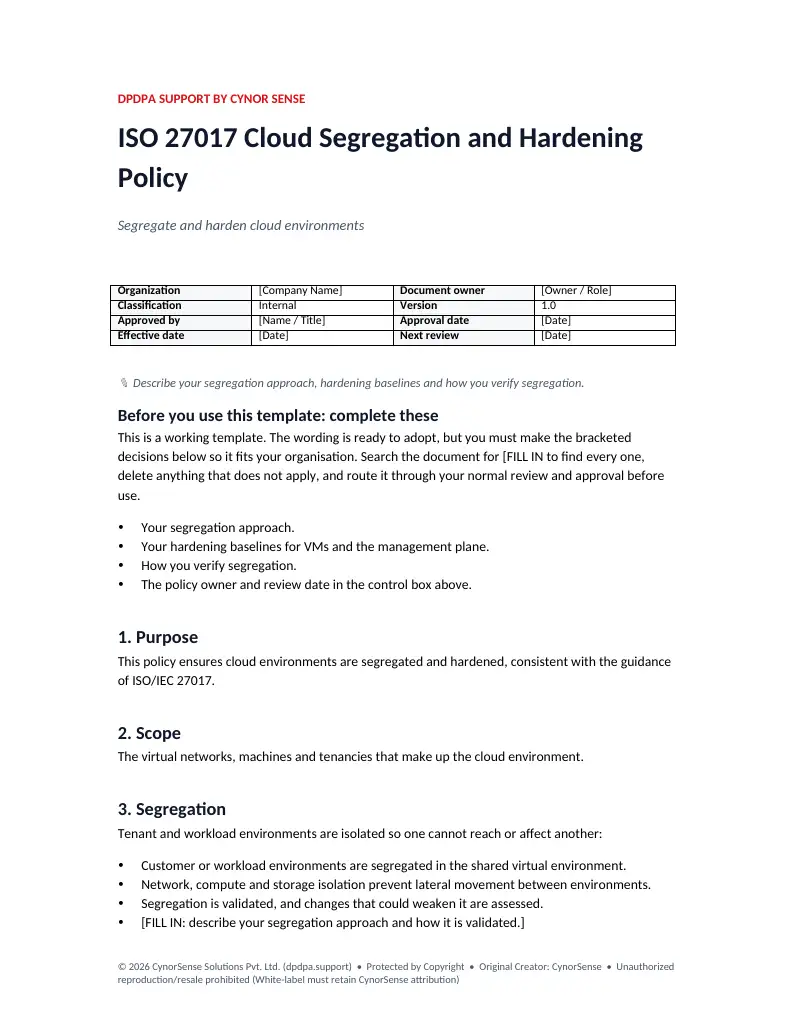 ISO 27017 Cloud Segregation Hardening Policy
✎ Describe your segregation approach, hardening baselines and how you verify segregation.
-
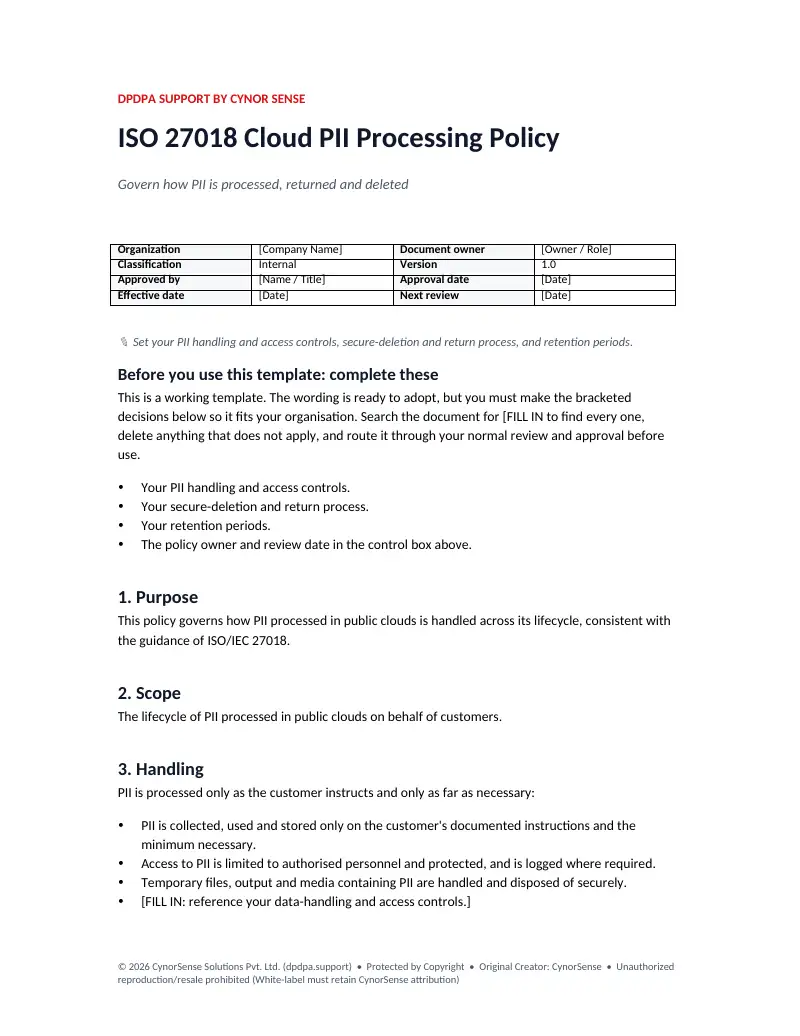 ISO 27018 Cloud PII Processing Policy
✎ Set your PII handling and access controls, secure-deletion and return process, and retention periods.
-
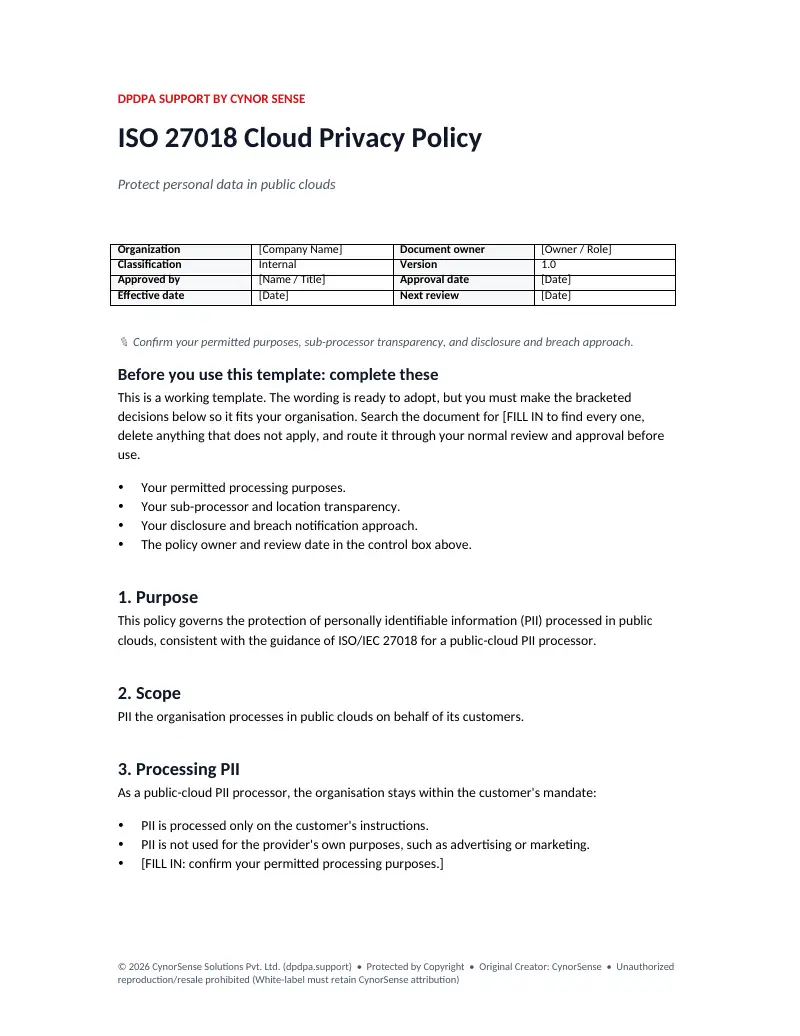 ISO 27018 Cloud Privacy Policy
✎ Confirm your permitted purposes, sub-processor transparency, and disclosure and breach approach.
₹5,999 incl. GST
How the files fit together
A suggested order
Our suggestion, not a requirement of the standard or the law.
- 1
Find the gaps
Start with the assessment workbooks to see where you stand.
2 files: ISO 27017 Cloud Security Gap Assessment, ISO 27018 Cloud Privacy Gap Assessment
- 2
Approve the policies
Edit the policies to match how you work, then get them approved.
6 files: ISO 27017 Cloud Administrator Operations Policy, ISO 27017 Cloud Exit Data Return Policy, ISO 27017 Cloud Security Policy, ISO 27017 Cloud Segregation Hardening Policy and more
- 3
Keep the records
Keep the registers and logs up to date as evidence for an audit or a review.
1 file: ISO 27017 Cloud Shared Responsibility Matrix
Questions
Before you buy
What exactly do I get?
9 editable files (7 Word, 2 Excel). Every file is listed on this page with its file name, size and number of sections.
How are the files delivered?
Digitally, after your payment is confirmed: we email download links to the address you gave at checkout. Each link works for 2 hours; you can ask for a fresh one from My purchases. Nothing is shipped.
How do I pay?
Through Razorpay, by UPI, card or netbanking.
Is GST included?
Yes. The price includes GST. To get a GST invoice, email [email protected] with your billing name, address and GSTIN.
Are these official documents of the standard body or regulator?
No. They are templates supplied by CynorSense Solutions Pvt. Ltd. They are not issued or endorsed by any standard body or regulator, and they are not legal advice. Using them does not by itself make an organisation compliant or certified.